Ethical Hacking Certificate Program in Jalandhar
Learn offensive security, finding the holes before somebody else does, taught on live client work at techcadd Jalandhar rather than from slides.
- Live client projects
- Practitioner trainers
- Placement support
- Certificate + internship
- Duration
- 3 – 6 Months
- Mode
- Classroom, Weekend & 1-on-1
- Eligibility
- 12th Pass Onward
- Includes
- Internship Letter
- Students trained
- 25,000+Students trainedsince 2016
- Google rating
- 4.9★Google rating556+ reviews
- Practical training
- 100%Practical traininglive client work
Course overview
techcadd's Ethical Hacking Certificate Program in Jalandhar, run over 3 to 6 months, takes students and IT professionals through offensive security in the order a real assessment actually runs. You begin with reconnaissance and footprinting, then scanning, enumeration and exploitation using Nmap and Metasploit. System hacking and privilege escalation follow, then web application attacks including SQL injection, worked through in Burp Suite. Wireless and network attacks are covered practically, along with the social engineering techniques that account for a large share of real incidents. Later modules introduce malware analysis fundamentals and password attacks with John the Ripper and Hydra. The programme closes on reporting and responsible disclosure, because a finding nobody can reproduce or act on is worth very little. All lab work runs on Kali Linux inside a controlled environment with a trainer supervising. You leave with written assessment reports, CV preparation and interview practice for Penetration Tester, Security Analyst or bug bounty work.
Think like an attacker,work as a defender
Ethical hacking means testing computers, networks and websites for weaknesses, with the owner's written permission, so they can be fixed before a criminal finds them. The skills look like hacking; the purpose, the permission and the report at the end are what make it a profession.
Think of a locksmith hired by a jewellery shop in Jalandhar to try every door and window after closing time. If they get in, they do not take anything: they write down exactly how, so the shop can fix it. That is an ethical hacker. This course trains you to run that kind of test properly, from first look to final report. Each field below shows how much of it the course covers.
- Job-ready focus2 fields
- The course trains you for entry-level work in this field.
- Strong foundation2 fields
- You learn the base skills here; one specialised course makes you job-ready.
- Introduced2 fields
- You will use it in the course, but it is not a specialisation.
- Not covered1 field
- Not part of this course; available as a separate techcadd course.
What this course makes you job-ready for
Job-ready focusPenetration Testing & Vulnerability Assessment (VAPT)
A structured, permitted test of a company's systems: map what exists, find the weaknesses, safely prove which ones are real, and hand over a report with fixes ranked by risk.
An immigration consultancy stores passport scans online. Before an audit, it hires a tester who finds an outdated server and a weak admin password, and reports both with clear fixes.
- Ethical Hacking tools used
- Kali LinuxNmapMetasploitWiresharkHydraJohn the Ripper
- Job roles
- Penetration TesterEthical HackerVulnerability Assessment Analyst
Months 1–2 (reconnaissance, scanning, enumeration, exploitation, privilege escalation) and Month 4 (reporting and responsible disclosure). Projects: Ethical Hacking Fundamentals Build, Live Client Brief.
Web Application Security Testing
Testing websites and web apps (login pages, forms, shopping carts, admin panels) for flaws such as SQL injection that can expose customer data.
Checking an online store's search box to make sure nobody can type something into it that pulls out every customer's address and phone number.
- Ethical Hacking tools used
- Burp SuiteNmapKali Linux
- Job roles
- Web Application Security TesterVAPT Analyst
Months 2–3 (web application attacks and SQL injection in Burp Suite). Project: Real-World Data Challenge.
What this course lays the foundation for
Strong foundationBug Bounty Hunting
Finding security flaws in companies' public websites and apps through their official bug bounty programmes, and getting rewarded when a valid finding is reported responsibly.
Reporting a flaw in a large company's mobile banking website through its published programme, following its rules exactly.
- Ethical Hacking tools used
- Burp SuiteNmapreporting templates
- Job roles
- Bug Bounty Hunter (freelance)Security Researcher
Web testing (Months 2–3) and reporting and responsible disclosure (Month 4) are the core skills. Earning from bug bounties takes months of extra independent practice on legal platforms after the course.
Network & Wireless Security Testing
Testing an office's internal network and Wi-Fi to see whether an outsider, or a visitor in the waiting room, could get onto systems they should not reach.
Showing a school that its guest Wi-Fi lets visitors see the office printers and the accounts PC.
- Ethical Hacking tools used
- NmapWiresharkKali Linux
- Job roles
- Network Penetration TesterSecurity Analyst
Months 2–3 (wireless and network attacks). Designing and configuring secure networks yourself is taught in techcadd's Network Security & CCNA course.
What this course introduces
IntroducedSocial Engineering & Security Awareness
Understanding how attackers trick people rather than machines: fake calls, phishing emails and messages, and training staff to recognise them.
Running an approved phishing-awareness exercise for a hospital's staff and then teaching them what the warning signs were.
- Ethical Hacking tools used
- Awareness training materialapproved simulation platforms
- Job roles
- Security Awareness TrainerSecurity Analyst
Months 2–3 (social engineering techniques), taught for awareness and authorised testing only.
Malware Analysis
Studying malicious software in a safe, isolated lab to understand what it does, how it spreads and how to detect it.
Examining a suspicious attachment from an email in an isolated lab to see which files and websites it tries to reach.
- Ethical Hacking tools used
- Isolated lab machinesWireshark
- Job roles
- Malware Analyst (junior)SOC Analyst
Month 4 (malware analysis fundamentals). Deeper analysis and forensic investigation are taught in techcadd's Cyber Forensics course.
Not part of this course
Not coveredSecurity Operations (SOC) & Monitoring
The defensive side: watching alerts in a SIEM tool around the clock, investigating them and responding to real attacks as they happen.
A SOC analyst notices unusual logins on a bank's server late at night and escalates them within minutes.
- Ethical Hacking tools used
- SplunkMicrosoft SentinelMITRE ATT&CK
- Job roles
- SOC AnalystIncident Responder
Not part of this course. Knowing how attacks work helps a lot in SOC interviews, and the SIEM and monitoring skills are taught in techcadd's SOC Analyst and Cybersecurity programmes.
Clearing up common confusions
Is ethical hacking the same as penetration testing?
They overlap almost completely. “Ethical hacking” is the broad skill; “penetration testing” is the formal, scoped engagement a company pays for, with a contract and a report. Job adverts mostly say Penetration Tester or VAPT Analyst.
Bug bounty is not a guaranteed income.
Only valid, original findings within a programme's published scope are paid, and many beginners earn little for a long time. Treat it as practice and a portfolio builder alongside a job, not as a replacement for one.
Ethical hacking skills also help in…
Red teaming (long, realistic attack simulations against a whole organisation), cloud security testing, mobile app testing and secure software development. These need experience beyond a first course, but the method you learn here, recon to report, is the same in all of them.
At a glance: what this course covers
| Field | Coverage in this course | Where you learn it | Next step at techcadd |
|---|---|---|---|
| Penetration Testing & VAPT | Job-ready focus | Months 1–2, 4; Live Client Brief | Ready to apply |
| Web App Security Testing | Job-ready focus | Months 2–3 | Ready to apply |
| Bug Bounty | Strong foundation | Months 2–4 | Independent practice on legal platforms |
| Network & Wireless Testing | Strong foundation | Months 2–3 | Network Security & CCNA |
| Social Engineering Awareness | Introduced | Months 2–3 | — |
| Malware Analysis | Introduced | Month 4 | Cyber Forensics |
| SOC & Monitoring | Not covered | — | SOC Analyst or Cybersecurity |
| Cloud Security | Not covered | — | Cybersecurity programme |
Which Ethical Hacking pathsuits you?
Ethical hacking is a good fit for curious people who like to understand how things really work. Everyone starts with the same recon-to-report method; this guide helps if you already have a direction in mind:
| If you… | You will probably enjoy | Typical first job |
|---|---|---|
| Like puzzles and trying every possible way in | Penetration Testing | Junior Penetration Tester, VAPT Analyst |
| Spend time on websites wondering how they work underneath | Web Application Security | Web Security Tester |
| Want to work independently and get rewarded per finding | Bug Bounty Hunting | Bug bounty alongside a security job |
| Prefer defending and watching for attacks over attacking | SOC & Monitoring | SOC Analyst (take the SOC Analyst course instead) |
| Enjoy writing clear reports and explaining risks to clients | Security Consulting | Security Analyst, Junior Consultant |
| Are not sure yet | Start with this course or the Cybersecurity programme | Decide with a counsellor after a free demo class |
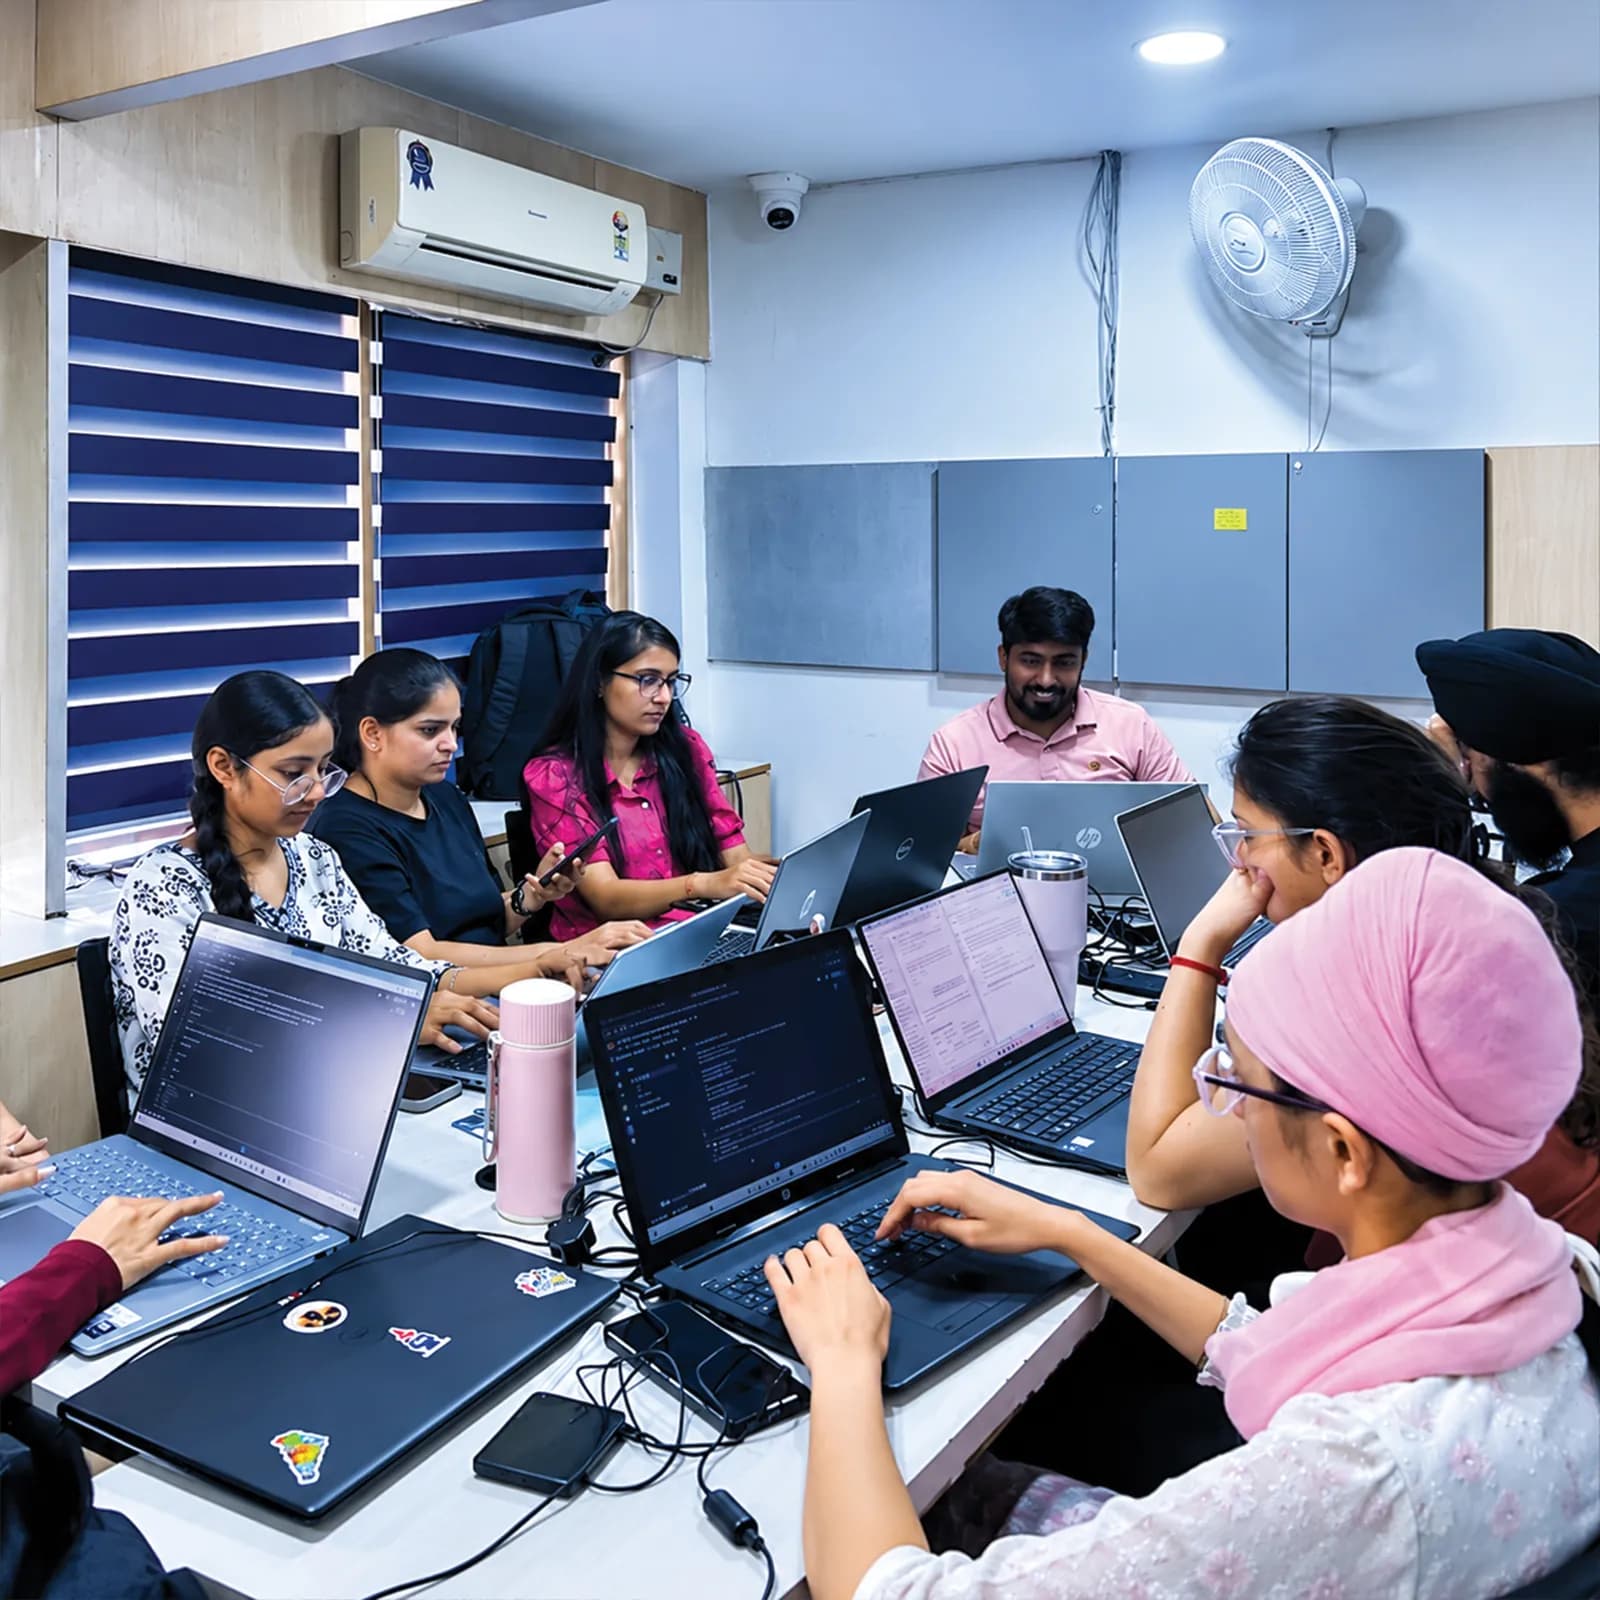
Industry-Ready Training in Ethical Hacking
- 100% practical, project-based learning
- AI tools integrated into every module
- Live client projects under trainer supervision
- Internship letter and placement support
- Small batches with daily doubt clearing
What you will
actually build
The syllabus is arranged so every module produces an asset rather than a set of notes. You will cover reconnaissance and footprinting, scanning, enumeration and exploitation, system hacking and privilege escalation, web application attacks and SQL injection, wireless and network attacks, and finish with a live project built on Kali Linux, Metasploit, Burp Suite. Months 1–2 cover foundations and core skills; Month 3 moves into applied work on live client projects under supervision; the final phase closes with portfolio preparation and placement support that turn all of it into an offer letter.
Foundation: Reconnaissance to System Hacking
- Reconnaissance and footprinting
Passive and active information gathering on a target before any exploit runs — the step that decides how much of a later attack even works, done inside the isolated Kali Linux lab.
- Scanning, enumeration and exploitation
Nmap scans mapping open ports and services, then Metasploit turning a found vulnerability into an actual exploit, the sequence a real penetration test follows.
- System hacking and privilege escalation
Escalating from an initial low-privilege foothold to full system access, the step that separates a superficial finding from a genuinely critical one in a client report.
Useful for: Penetration Testing and VAPT. This is the method every test follows.
Ethical Hacking Is Powering the Next Generation of Industry Leaders
- Live client work from week one, supervised by a trainer, not slides, not simulations.
- Penetration Tester roles in Punjab start around ₹20,000 – ₹38,000 a month for a fresher with a working portfolio.
Reviewed by mentors. Built for interviews.Who can dothis course
The Ethical Hacking programme is built for people at six different starting points, and the batch is deliberately mixed. What matters far more than your background is turning up consistently and finishing what each module asks you to build.
Students after 12th
Join from any stream. You start from fundamentals with no assumed knowledge, and most students run the programme alongside a degree at a Jalandhar college using the weekday or weekend batch.
Graduates and final-year students
If you are finishing a BA, BBA, B.Com, BCA or B.Tech, this is the shortest route from degree to salary. Enter placement season with project work in hand instead of a blank CV.
Working professionals
The weekend batch exists for people already earning. Career switchers typically become interview-ready for Penetration Tester roles within five to six months without leaving their current job.
Business owners and freelancers
Owners take this programme to stop outsourcing work they cannot judge. Freelancers take it to bill clients beyond Punjab, since location does not limit remote work in this field.
Career restarters
A gap on the CV counts for less than work you can point at. The programme starts at zero and finishes with a portfolio and a documented internship letter, which is what an interviewer asks about after a break.
Self-taught learners
If free videos left you with notes but nothing built, what changes here is a trainer who reviews what you produced this week and a deadline attached to every module.
One course.A mesh of real tools.
Everything below is installed on the lab machines and used on live client work, not shown once in a slide and forgotten.
- Kali Linux
- The Linux system testers use, with security tools pre-installed
- Metasploit
- A framework for safely testing known weaknesses in a lab
- Burp Suite
- Sits between browser and website to test web apps for flaws
- Nmap
- Finds which devices and services are running on a network
- Wireshark
- Captures network traffic so you can see what is being sent
- John the Ripper
- Audits password strength by testing password hashes
- Hydra
- Tests how well login systems resist password guessing
Get Certified in
Ethical Hacking
Complete the course with a portfolio of live projects and receive an industry-recognised certificate, plus a documented internship letter accepted by Punjab universities.
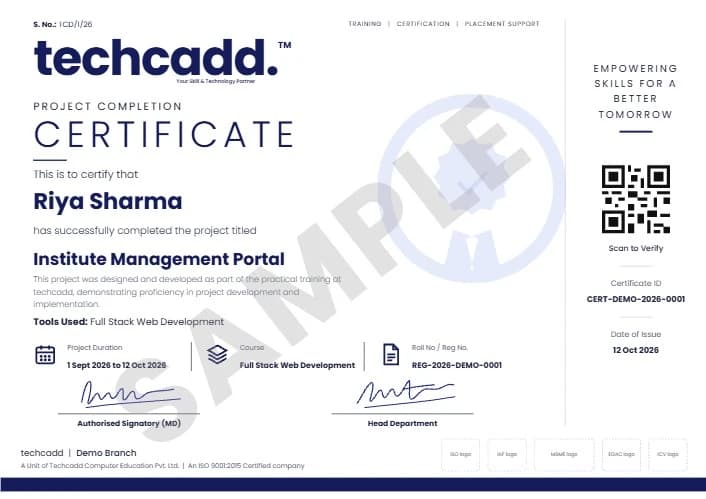
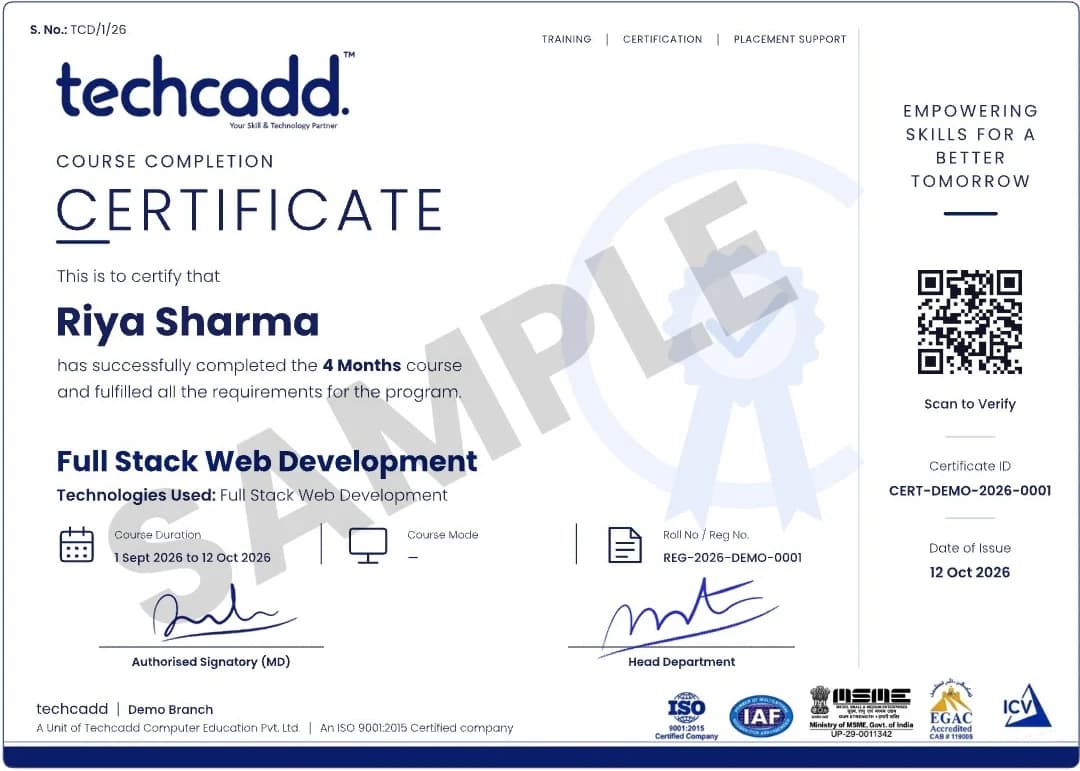
Two certificates on completion — the course certificate and a separate capstone project certificate.
Where this coursetakes you
The roles this opens, what they pay in Punjab and beyond, and who is hiring for them — the same figures our free Salary Estimator publishes, not a brochure number.
Cybersecurity Analyst
Protects networks, applications, and data from security threats.
- Starting package
- ₹2.5–4.5LPA
- After 2 years
- ₹5–9LPA
Indicative ranges for Cybersecurity Analyst roles, compiled from public job-market listings and drawn on the same scale in every market. Actual offers vary by employer, skillset and interview performance — Punjab pay typically reaches 2× the fresher ceiling within two years of delivery experience.
Open the salary estimatorWhere Cybersecurity Analyst graduates get hired
- SOC teams at IT services and BPO companies
- Banks, insurance and fintech security teams
- Government and defence contractors
- Bug bounty platforms and freelance pen-testing
What job roles open up after Ethical Hacking?
Most companies in Punjab buy penetration testing as a service, so jobs sit with security firms, IT service companies and consultancies, and freelance work is common. The roles fall into two groups:
- Junior Penetration Tester
- Ethical Hacker
- VAPT Analyst
- Web Application Security Tester
- Bug Bounty Hunter (alongside a job)
- SOC Analyst (with SOC Analyst course)
- Network Security Engineer (with Network Security & CCNA course)
- Digital Forensics Analyst (with Cyber Forensics course)
- Cloud Security Engineer (with Cybersecurity programme)
- Security Consultant (with Penetration Testing course and experience)
What job roles open up after Ethical Hacking?
Graduates move into Penetration Tester, Ethical Hacker, Security Analyst, Bug Bounty Hunter and similar roles. Penetration testing is billable consulting work, and certified testers are scarce across Punjab.
What can I earn, and how fast does it grow?
A fresher with a working portfolio starts around ₹20,000 – ₹38,000 a month in the Jalandhar market. With two years of delivery experience that typically doubles, and specialists who keep learning move well beyond it.
Can I freelance or work remotely with this skill?
Yes. A Jalandhar address costs you nothing on a remote brief. Students bill clients in Delhi, Dubai and Canada. The programme covers client handling, proposals and reporting so you can price and defend your work, not just do it.
Which industries hire for this in Punjab?
Beyond IT companies, the export houses, sports goods and hand tool manufacturers, immigration consultancies, hospitals, schools and real estate firms across Jalandhar all now hire for these skills directly.
Can I continue to higher studies or a specialisation later?
The certificate and portfolio stand on their own, and they stack. Most students move on to an adjacent techcadd track. The tools overlap, so the second programme is faster than the first.
Your Ethical Hacking careerroadmap
This course is Step 1 for the offensive side of security. For testing roles it is enough on its own; for other security roles you add one focused course. Here is how each path looks:
| Goal | Step 1 | Step 2 | Where you arrive |
|---|---|---|---|
| Penetration Tester | Ethical Hacking Certificate Program | Ready to apply | Junior Penetration Tester |
| Senior / scoped VAPT work | Ethical Hacking Certificate Program | Penetration Testing | Penetration Tester, Security Consultant |
| SOC Analyst | Ethical Hacking Certificate Program | SOC Analyst | SOC Analyst L1 |
| Network Security Engineer | Ethical Hacking Certificate Program | Network Security & CCNA | Network Security Engineer |
| Digital Forensics Analyst | Ethical Hacking Certificate Program | Cyber Forensics | Digital Forensics Analyst |
| All-round security career | Ethical Hacking Certificate Program | Cybersecurity (adds SOC, cloud security and AI automation) | Cybersecurity Analyst |
Hands-on projectsyou will ship
Ethical Hacking Fundamentals Build
Your first working piece, applying reconnaissance and footprinting and scanning, enumeration and exploitation end to end rather than as isolated exercises.
Field: Penetration Testing, VAPT
Real-World Data Challenge
Work with messy, real inputs (web application attacks and sql injection and wireless and network attacks) and defend the choices you made to a trainer.
Field: Web Application Security, Wireless Testing
Live Client Brief
A genuine requirement from techcadd's delivery pipeline, scoped, built and shipped under supervision. This is the one interviewers ask about.
Field: Penetration Testing, Security Consulting
Portfolio Capstone
A ethical hacking project you specify yourself, covering malware analysis fundamentals and deployment, and present as your final piece.
Field: Your chosen speciality, with reporting
Learn it. Build it. Make it yours.
Every project moves through the same loop: understand the brief, build with guidance, then explain the decisions behind your work.
Understand
Break a real requirement into a clear plan and the right tools.
Ethical Hacking Fundamentals BuildBuild
Work hands-on with trainer feedback while the decisions are still easy to change.
Real-World Data ChallengePresent
Turn the finished work into a portfolio story you can defend in an interview.
Live Client BriefWhy students choosetechcadd
There are many places to learn this in Jalandhar and the brochure syllabus looks similar at all of them. What differs is who teaches, whether you ever touch real work, and whether anyone picks up the phone after you have paid. techcadd has trained students across Punjab since 2016 on the same model: small batches, working practitioners as trainers, client projects as coursework.
Trainers who still do the work
Your trainer is not a full-time lecturer. They deliver client projects for techcadd's services arm, so examples in class are current rather than a case study from five years ago.
Live projects, real consequences
You work on genuine client requirements under supervision. This is where a portfolio comes from, and it is the first thing an interviewer asks to see.
Small batches and open lab hours
Batches stay small enough that a trainer sees your screen daily. Lab time runs outside class hours and doubt sessions continue until the concept lands.
Internship letter and certificate
Every student finishes with an industry-recognised certificate and a documented internship on real work, accepted for university industrial training requirements.
A placement cell that persists
Mock interviews, CV reviews and drives with hiring partners across Jalandhar and Ludhiana, repeated after a rejection, not abandoned.
Since 2016, 25,000+ students
A decade of hiring relationships in Punjab is why a call from our placement cell gets answered and why local employers know what our certificate means.
How techcaddcompares
Security training is the easiest subject to fake and the hardest to verify. These are the eight things worth asking before you pay any institute, including this one.
| Feature | techcadd | Other institutes |
|---|---|---|
| Curriculum | Industry-aligned, updated regularly | Often outdated or generic |
| Learning style | 100% hands-on, project-based | Mostly theory-heavy |
| Trainers | Industry-experienced mentors who still deliver client work | Mixed experience levels |
| Real projects | Multiple real-world projects plus a capstone | Limited or simulated projects |
| Practice lab | An isolated lab you attack legally, with every exercise written up as a professional finding | Tool tours with nothing to attack |
| Placement support | Dedicated career and interview preparation | Often limited or absent |
| Batch flexibility | Weekday, evening, weekend and 1-on-1 options | Fixed schedules |
| Doubt support | Ongoing mentor and community support | Limited post-class support |
| Certification | Industry-recognised certificate plus a documented internship letter | Varies |
The right-hand column describes what is commonly offered in the market, not any particular institute. Ask any institute you are considering — this one included — to show you the work its students actually produced.
What our studentsin Jalandhar say
- Google
techcadd's placement cell kept calling me for drives until I was placed. That persistence mattered more than the certificate for Ethical Hacking.
Anjali VermaCareer Switcher · Jalandhar Cantt GoogleI was switching careers and worried I would be behind. Half the Ethical Hacking batch were doing the same thing, and nobody made me feel slow.
Gurpreet DhillonWorking Professional · Nakodar GoogleI joined the Ethical Hacking batch with almost no background and finished with a project I could actually show. The trainers correct your work daily rather than just moving to the next slide.
Manpreet KaurFinal-Year Student · Hoshiarpur Googletechcadd's placement cell kept calling me for drives until I was placed. That persistence mattered more than the certificate for Ethical Hacking.
Anjali VermaCareer Switcher · Jalandhar Cantt GoogleI was switching careers and worried I would be behind. Half the Ethical Hacking batch were doing the same thing, and nobody made me feel slow.
Gurpreet DhillonWorking Professional · Nakodar GoogleI joined the Ethical Hacking batch with almost no background and finished with a project I could actually show. The trainers correct your work daily rather than just moving to the next slide.
Manpreet KaurFinal-Year Student · Hoshiarpur
- Google
What made Ethical Hacking click for me was the lab time. You can sit after class and someone will still explain it until you get it.
Vikas ChopraWeekend Batch · Ludhiana GoogleThe Ethical Hacking programme got me interview-ready faster than I expected. My interviewer asked to see my project and that was the whole conversation.
Neha BansalPlaced Fresher · Jalandhar GoogleI travelled in for the weekend Ethical Hacking batch and it was worth every trip. Small batch, real work, no time wasted on theory nobody uses.
Arshdeep SinghTrainee Engineer · Adampur GoogleWhat made Ethical Hacking click for me was the lab time. You can sit after class and someone will still explain it until you get it.
Vikas ChopraWeekend Batch · Ludhiana GoogleThe Ethical Hacking programme got me interview-ready faster than I expected. My interviewer asked to see my project and that was the whole conversation.
Neha BansalPlaced Fresher · Jalandhar GoogleI travelled in for the weekend Ethical Hacking batch and it was worth every trip. Small batch, real work, no time wasted on theory nobody uses.
Arshdeep SinghTrainee Engineer · Adampur
Frequently Asked Questions
techcadd runs Ethical Hacking over 3 to 6 months depending on the track you choose. Weekday, evening and weekend batches cover the same syllabus, and 1-on-1 training is available if you would rather set your own pace. Every class runs for 2 hours, whichever format you choose.
Fees depend on the course length and subject. techcadd counsellors share the exact fee for the length you choose and EMI options on request, and a demo class is free.
Students after 12th, graduates and final-year students, working professionals switching careers, and business owners all join this programme. You start from fundamentals, so a technical background helps but is not required.
Graduates typically move into roles such as Penetration Tester, Ethical Hacker, Security Analyst or Bug Bounty Hunter. Penetration testing is billable consulting work, and certified testers are scarce across Punjab.
A fresher with a working portfolio typically starts around ₹20,000 – ₹38,000 per month in the Jalandhar market, rising substantially within two years of experience. Freelancers handling multiple clients often earn more, since remote work is not limited by location.
No training provider can honestly guarantee a job, and you should be cautious of anyone in Jalandhar who claims one. techcadd guarantees placement support: CV reviews, mock interviews, portfolio preparation and repeated drives with hiring partners across Jalandhar and Ludhiana.
You will work hands-on with Kali Linux, Metasploit, Burp Suite, Nmap, Wireshark, John the Ripper and the supporting toolchain used on live projects. All practice happens in the lab on licensed software, not on demo screenshots.
Yes. Every student receives an industry-recognised certificate on completion plus a documented internship letter based on live client work. The internship satisfies the industrial training requirement at most Punjab universities.
Every module ends with something you built. The Ethical Hacking Certificate Program finishes with a live project drawn from techcadd's own client delivery work, supervised by a trainer, which becomes the portfolio you take to interviews.
Yes. techcadd Jalandhar runs weekday, evening and weekend batches in parallel so working professionals and college students can both attend, and 1-on-1 training is available for a fully personal schedule. Every class (batch or 1-on-1) runs for 2 hours; book a free demo class to see the lab and meet the trainer before enrolling.
Yes, when you have the system owner's clear, written permission and stay within the agreed scope. Testing anything without permission is an offence under the IT Act, whatever your intention. In this course you practise only in techcadd's isolated lab and on platforms built for legal practice.
No. This course covers the offensive side: recon, exploitation, web and wireless testing and reporting. The Cybersecurity programme covers this plus the defensive side (SOC and SIEM), cloud security and AI automation over nine months. Choose this if you are sure you want to be a tester.
Not directly. SOC work is defensive: monitoring alerts in a SIEM and responding to incidents, which this course does not teach. Understanding attacks does help in SOC interviews, and you can add techcadd's SOC Analyst course to cover that side.
Some students do, but most need months of extra practice first. The course gives you the web testing and reporting skills that bug bounty work needs. Treat bounties as practice and portfolio building alongside a job, not as a guaranteed income.
Ethical hacking is the broad skill of testing systems with permission. Penetration testing is the formal, contracted engagement with a defined scope and a written report. This course teaches the skills; techcadd's Penetration Testing course goes deeper into running full engagements.
It includes malware analysis fundamentals, but not forensic investigation such as recovering evidence from disks, memory or phones for legal cases. That is taught in techcadd's Cyber Forensics course.
Every module,stage by stage
The Ethical Hacking Certificate Program syllabus runs as 3 stages inside one enrolment. A tick shows the stage each capability first appears in — the ladder is cumulative, so a later stage builds on the earlier ones instead of replacing them.
Foundations & Core Skills
6 capabilities
Opens with Reconnaissance and footprinting through Social engineering techniques. 6 capabilities, taught, practised in the lab and assessed on work you keep.
Applied Work
+2 capabilities
Adds Malware analysis fundamentals through Reporting and responsible disclosure, on top of everything stage 1 already covers.
Live Project & Placement Prep
+4 capabilities
Adds A live client project you keep in your portfolio through Placement drives with our hiring partner network, on top of everything stage 2 already covers.
| Module | Stage 1 | Stage 2 | Stage 3 |
|---|---|---|---|
| 01Reconnaissance and footprintingTaught in the foundations stage, with a graded exercise you keep. | Included | Included | Included |
| 02Scanning, enumeration and exploitationPart of foundations — practised in supervised lab time, not just demonstrated. | Included | Included | Included |
| 03System hacking and privilege escalationBuilt hands-on in the foundations stage and reviewed line by line. | Included | Included | Included |
| 04Web application attacks and SQL injectionCovered under core skills, with lab work you can show in an interview. | Included | Included | Included |
| 05Wireless and network attacksAssessed on what you produce in the core skills stage, not on notes. | Included | Included | Included |
| 06Social engineering techniquesWorked through in the core skills stage and carried into your project. | Included | Included | Included |
| 07Malware analysis fundamentalsTaught in the applied work stage, with a graded exercise you keep. | Not included | Included | Included |
| 08Reporting and responsible disclosurePart of applied work — practised in supervised lab time, not just demonstrated. | Not included | Included | Included |
| 09A live client project you keep in your portfolioBuilt hands-on in the live project & placement prep stage and reviewed line by line. | Not included | Not included | Included |
| 10Documented internship on real workCovered under live project & placement prep, with lab work you can show in an interview. | Not included | Not included | Included |
| 11CV review, mock interviews and aptitude drillsAssessed on what you produce in the live project & placement prep stage, not on notes. | Not included | Not included | Included |
| 12Placement drives with our hiring partner networkWorked through in the live project & placement prep stage and carried into your project. | Not included | Not included | Included |
Every stage sits inside the one programme: nothing is dropped as you move up, and nothing is charged for twice. If you are not sure which stage matters most for the role you are aiming at, a counsellor will map it against the jobs actually hiring in Punjab right now.
Not sure which ethical hacking path is right for you?
One call with a counsellor usually settles it. Tell us whether you like attacking, defending or investigating, and we will show you whether this course, the SOC Analyst course or the full Cybersecurity programme fits you. Book a free demo class and see the lab first.
Ask aboutEthical Hacking
Send your question and a counsellor will call you back about batch timings, fees, EMI options, placement record, or whether this course fits your degree.
- Free counselling and demo class
- Weekday, evening, weekend or 1-on-1, all 2-hour classes
- Internship letter and placement support