Cloud Computing Certificate Program in Jalandhar
Learn deploying and running infrastructure on AWS and Azure instead of a server in the office, taught on live client work at techcadd Jalandhar rather than from slides.
- Live client projects
- Practitioner trainers
- Placement support
- Certificate + internship
- Duration
- 3, 6 or 9 Months
- Mode
- Classroom, Weekend & 1-on-1
- Eligibility
- 12th Pass Onward
- Includes
- Internship Letter
- Students trained
- 25,000+Students trainedsince 2016
- Google rating
- 4.9★Google rating556+ reviews
- Practical training
- 100%Practical traininglive client work
Course overview
Cloud computing turns infrastructure into a service. Instead of buying and maintaining every server, storage system and network device yourself, you provision computing resources on demand, scale them as workloads change, secure them through policy, automate them as code, and pay only for what you use. Four properties define it: on-demand provisioning, scalability up and down with demand, pay-as-you-go pricing, and high availability built on distributed infrastructure with backups and redundancy.
The work itself runs on a loop — plan the workload, provision the cloud resources, deploy the applications, then monitor and improve — and four capabilities make a cloud engineer: compute (EC2, containers and scalable workloads), network (VPC, subnets, routing and security), storage (S3, EBS, EFS and databases) and automation (Terraform, CI/CD and monitoring). The most valuable skill is knowing which service and architecture a problem actually needs: not every application requires Kubernetes, multiple servers or a complex setup, and a simple one may only need a virtual machine, storage, a database and proper networking. Traditional infrastructure still wins where you need complete control over dedicated hardware, predictable workloads or specific compliance requirements.
techcadd's Cloud Computing Certificate Program in Jalandhar is a single 25-module ladder taught in Jalandhar, with exit points at three, six and nine months. Module 01 begins with Linux administration, and Bash scripting, networking and Git follow from the ground up, so no coding background is assumed; from Module 05 onward every session runs on live AWS. Stage 1 covers IAM, VPC design, EC2 compute, storage and databases, scaling and high availability, ending in a complete multi-tier AWS capstone. Stage 2 adds serverless and event-driven AWS, security engineering and disaster recovery, AI and generative-AI services on AWS, Docker, Kubernetes, Jenkins, Terraform, observability and AI model deployment. Stage 3 is a structured extension that deepens the same domains: architecture and resilience engineering, security and compliance, production AI service engineering, Kubernetes operations at scale, GitOps automation, site reliability with cost optimisation, and MLOps with a final expert capstone.
Cloud teams need people who can move from Linux, scripting and networking fundamentals through AWS infrastructure, deployment, security, containers, automation, monitoring and production troubleshooting — and prove it with work they have actually built. Labs, projects, practical assessments, documentation, interview preparation and certification are built into every stage, so a learner leaves each track with artefacts that can be opened and defended, not only a certificate.
All lab work runs on real AWS accounts under trainer supervision rather than sandboxed simulations, and progression through the ladder is capability-gated: you advance when a deliverable passes review, not when the calendar says so. You finish each stage with deployed infrastructure you can walk an interviewer through, a documented internship letter, CV preparation and interview practice for Cloud Support Engineer, Cloud Engineer, DevOps Engineer or more senior cloud roles depending on the stage you complete.
One cloud foundation,many careers
Cloud computing means renting servers, storage, databases and networks over the internet instead of buying and running them yourself. Today almost every app, website and AI service runs on the cloud, so cloud skills sit underneath many different jobs: support, cloud engineering, DevOps, Kubernetes, security, reliability and MLOps. What changes from role to role is which part of the cloud you specialise in.
Think of it like electricity. A shop in Jalandhar does not build its own power station; it plugs into the grid and pays for what it uses. The cloud does the same for computing. This programme teaches you to plan, build, secure, automate and run that infrastructure on AWS, climbing a 25-module ladder with exits at 3, 6 and 9 months. Each field below shows how much this programme covers, and which stage of the ladder covers it.
- Job-ready focus4 fields
- The course trains you for entry-level work in this field.
- Strong foundation4 fields
- You learn the base skills here; one specialised course makes you job-ready.
- Introduced
- You will use it in the course, but it is not a specialisation.
- Not covered
- Not part of this course; available as a separate techcadd course.
What this course makes you job-ready for
Job-ready focusCloud Support & Operations
Keeping cloud systems healthy day to day: managing Linux servers, fixing access and network problems, watching dashboards and responding to alerts.
A client's website goes slow on a Monday morning. The support engineer logs in over SSH, checks CloudWatch, finds a full disk and fixes it within minutes.
- Cloud Computing tools used
- LinuxBashAWS IAMAmazon VPCAmazon EC2CloudWatch
- Job roles
- Cloud Support EngineerAWS Cloud TraineeCloud Operations Associate
Stage 1 (Modules 1–10): Linux administration, Bash scripting, networking, Git, IAM, VPC and EC2. Projects: Linux & Bash Automation Toolkit, Secure AWS Network.
Cloud Infrastructure Engineering (AWS)
Designing and building the servers, storage, databases and networks a business runs on AWS, so they are secure, scale with demand and stay available.
Moving a Punjab exporter's order system onto EC2 and RDS behind a load balancer, so it keeps working when two servers fail or traffic triples.
- Cloud Computing tools used
- Amazon EC2Amazon S3Amazon RDSDynamoDBAmazon VPCRoute 53AWS LambdaCloudFormation
- Job roles
- Cloud EngineerAWS Cloud EngineerJunior Cloud Engineer
Stage 1 storage, databases, scaling and the AWS capstone (Modules 9–10), then serverless and event-driven AWS in Stage 2 (Module 11). Projects: AWS Web Application, Scalable Cloud Architecture, Event-Driven Serverless Workflow.
DevOps, CI/CD & Infrastructure as Code
Automating how software is tested and released, and describing infrastructure in code so it can be rebuilt the same way every time.
A developer pushes a fix, and a Jenkins pipeline tests it, scans it, builds a Docker image and deploys it to Kubernetes without anyone copying files by hand.
- Cloud Computing tools used
- GitGitHub ActionsJenkinsSonarQubeTerraformAnsibleCloudFormation
- Job roles
- DevOps EngineerCloud/DevOps AssociateCloud Automation Engineer
Stage 2 CI/CD Pipelines & Infrastructure as Code (Module 17), deepened in Stage 3 Infrastructure Automation & GitOps Delivery (Module 23). Projects: Automated CI/CD Pipeline, Infrastructure as Code.
Containers & Kubernetes
Packaging applications into containers with Docker and running many of them together on Kubernetes, which restarts failed ones and scales them with demand.
A food-delivery app split into small services, each in its own container, scaled up automatically at dinner time on Amazon EKS.
- Cloud Computing tools used
- DockerKubernetesAmazon EKSHelm
- Job roles
- DevOps EngineerKubernetes EngineerPlatform Engineer (with experience)
Stage 2 Docker & Containerization and Kubernetes Orchestration & Helm (Modules 15–16), then Production Containers & Kubernetes Operations in Stage 3 (Module 22). Project: Containerized Application.
What this course lays the foundation for
Strong foundationCloud Security
Protecting cloud accounts, data and networks: tight permissions, encryption, threat detection and a tested plan for recovering when something goes wrong.
Finding an S3 bucket of customer documents that was accidentally made public, locking it down and setting an alert so it cannot happen silently again.
- Cloud Computing tools used
- AWS IAMKMSGuardDutySecurity HubWAFCloudTrail
- Job roles
- Cloud Security Engineer (with experience)Cloud Engineer with a security focus
IAM in Stage 1 (Module 6), Cloud Security, Encryption & Disaster Recovery in Stage 2 (Module 12) and AWS Security Engineering & Compliance in Stage 3 (Module 20). Project: Security & Recovery Review. Offensive security and SOC monitoring are not part of this programme.
Site Reliability & Observability
Keeping live systems reliable: setting uptime targets, building dashboards and alerts, handling incidents calmly and controlling cloud cost.
A Grafana dashboard shows error rates rising after a release. An alert reaches the on-call engineer, who rolls back before most users notice.
- Cloud Computing tools used
- PrometheusGrafanaCloudWatchElasticsearch
- Job roles
- Site Reliability Engineer (with experience)DevOps EngineerCloud Operations Engineer
Monitoring, Observability & MLOps Deployment in Stage 2 (Module 18) and Site Reliability, Observability & Cost Optimisation in Stage 3 (Module 24). Project: Cloud Operations Platform. SRE roles usually come after some time on the job.
Cloud AI Services & MLOps
Running AI on the cloud: building applications on managed AI services, and deploying, monitoring and updating machine-learning models in production.
A chatbot for a Jalandhar college, built on Amazon Bedrock, that answers admission questions from the college's own documents.
- Cloud Computing tools used
- Amazon BedrockSageMakerPythonFastAPIStreamlitDocker
- Job roles
- MLOps Engineer (with experience)Cloud AI EngineerCloud Engineer (AI workloads)
Stage 2 AI foundations, AWS AI Services & Bedrock and MLOps deployment (Modules 13, 14, 18), deepened in Stage 3 (Modules 21, 25). Projects: AI Cloud Chatbot, MLOps Deployment. Training your own models from scratch is taught in techcadd's Machine Learning course.
Cloud Solutions Architecture
Designing the whole system before it is built: which services to use, how they connect, how they survive failure and what they will cost.
Deciding that a hospital's records system needs a second region for disaster recovery, while its marketing website needs only one server and S3.
- Cloud Computing tools used
- AWS Well-Architected Frameworkmulti-AZ designCloudFrontElastiCache
- Job roles
- Cloud Solutions Architect AssociateCloud Architect (with experience)
Scaling and architecture in Stage 1 (Module 10) and Cloud Architecture & Resilience Engineering in Stage 3 (Module 19). Architect roles are usually given after years of hands-on work, so treat this as preparation rather than a direct job.
Clearing up common confusions
Does this programme teach AWS or Azure?
The modules and labs are built on AWS, the most widely listed cloud in Indian hiring. The ideas (virtual machines, networks, storage, identity, monitoring) are the same on every cloud, so they carry over to Microsoft Azure. For Azure-specific administration, techcadd's Microsoft Azure course covers it directly.
Is cloud computing the same as DevOps?
No, but they work together. Cloud computing is the infrastructure itself: servers, networks and storage rented from a provider. DevOps is how software is built, tested and released onto that infrastructure. This programme teaches the cloud first in Stage 1 and adds DevOps in Stage 2.
Will I become a Data Scientist or ML Engineer here?
No. This programme teaches you to deploy and run AI on the cloud, not to build or train machine-learning models yourself. That is the MLOps and cloud side of AI. Building models is what techcadd's Machine Learning and Data Science courses teach.
Cloud Computing is also used in…
Data engineering and analytics platforms, penetration testing and SOC monitoring, Microsoft Azure and Google Cloud administration, and application development. These are not part of this programme, but the Linux, networking and AWS skills you build here are what each of them sits on.
At a glance: what this course covers
| Field | Coverage in this course | Where you learn it | Next step at techcadd |
|---|---|---|---|
| Cloud Support & Operations | Job-ready focus | Stage 1, Modules 1–8 | Ready to apply (3-month track) |
| Cloud Infrastructure (AWS) | Job-ready focus | Stage 1–2, Modules 5–11 | Ready to apply |
| DevOps, CI/CD & IaC | Job-ready focus | Stage 2–3, Modules 17, 23 | Ready to apply (6-month track) |
| Containers & Kubernetes | Job-ready focus | Stage 2–3, Modules 15, 16, 22 | Ready to apply (6-month track) |
| Cloud Security | Strong foundation | Modules 6, 12, 20 | Cybersecurity, SOC Analyst |
| Site Reliability & Observability | Strong foundation | Modules 18, 24 | Experience on the job |
| Cloud AI & MLOps | Strong foundation | Modules 13, 14, 18, 21, 25 | Machine Learning course |
| Solutions Architecture | Strong foundation | Modules 10, 19 | Experience on the job |
| Microsoft Azure administration | Not covered | — | Microsoft Azure course |
Which Cloud Computing pathsuits you?
You do not need to choose a cloud role before you join. Everyone climbs the same Stage 1 foundation of Linux, networking and core AWS, and most students find their direction in Stage 2. If you already have an idea, this quick guide helps:
| If you… | You will probably enjoy | Typical first job |
|---|---|---|
| Like fixing problems and helping when something breaks | Cloud Support & Operations | Cloud Support Engineer, Cloud Operations Associate |
| Enjoy building servers, networks and storage that just work | Cloud Infrastructure Engineering | Cloud Engineer, AWS Cloud Engineer |
| Dislike doing the same task twice and want to automate it | DevOps, CI/CD & Kubernetes | DevOps Engineer, Cloud/DevOps Associate |
| Care about access, privacy and keeping data safe | Cloud Security | Cloud Engineer first, cloud security roles later |
| Are excited by AI and want to run it in production | Cloud AI Services & MLOps | Cloud Engineer (AI workloads), MLOps roles later |
| Like planning the big picture and weighing cost against risk | Solutions Architecture | Cloud Engineer first, Solutions Architect Associate later |
| Are not sure yet | Start with the 3-month Practitioner track | Decide with your trainer whether to extend once Stage 1 is done |
Industry-Ready Training in Cloud Computing
- 100% practical, project-based learning
- AI tools integrated into every module
- Live client projects under trainer supervision
- Internship letter and placement support
- Small batches with daily doubt clearing
What you will
actually build
The syllabus runs as a single ladder of 25 topics with three exit points: the six-month Professional track continues exactly where the three-month Practitioner track ends, and the nine-month Expert track continues where the Professional track ends. Month 1 begins with Linux administration, Bash scripting, networking and Git from the ground up, so no coding background is assumed; from topic 05 onward every session runs on live AWS. Every topic is specified the same way — the subject matter, the named tool stack used in labs, the production problem the skill solves, and a practical artefact for your portfolio — and you advance when a deliverable passes review rather than when the calendar says so.
Foundation: Linux, Networking, Git & Core AWS (Topics 1–10)
- Linux Administration & File Systems
Linux architecture, kernel, shell and user space; distributions and release models; installation on virtual machines and cloud instances; the file system hierarchy, links and inodes; core commands for navigation, search, archiving and compression; redirection, pipes and filters with grep, awk and sed; users, groups, ownership, permissions, umask, sudo and access control lists; package management with apt, yum and dnf; processes, services and unit files under systemd; disks, partitions, mounting, /etc/fstab and swap; SSH key-based authentication; cron and scheduled jobs; log locations, journalctl and first-line troubleshooting.
- Bash Scripting & Server Automation
Shell scripting fundamentals; the shebang, execution permissions and PATH; variables, quoting, expansion and command substitution; positional parameters and argument parsing; standard input, output and error; exit codes; conditionals and loops; functions, scope and return values; arrays; text-processing pipelines for log analysis; here-documents; error handling with set -euo pipefail and trap; debugging with set -x; backup, log-rotation, user-provisioning and health-check scripts; scheduling with cron and systemd timers.
- Computer Networking & Protocols
LAN, WAN, MAN and PAN; topologies; routers, switches, firewalls and gateways; the OSI and TCP/IP models layer by layer; encapsulation and framing; IPv4 and IPv6 addressing, CIDR notation and hands-on subnetting; MAC addressing and ARP; DNS hierarchy, resolution and record types; DHCP; NAT and port address translation; static and dynamic routing; TCP versus UDP, the three-way handshake and common service ports; HTTP, HTTPS and TLS basics; VPN types; troubleshooting with ping, traceroute, dig, netstat, ss, curl and tcpdump.
- Git, GitHub & Version Control Workflow
Version control concepts and why infrastructure belongs in it; repositories, the staging area and the commit graph; inspecting history with log, diff and blame; branching, merging, rebasing and conflict resolution; .gitignore and repository hygiene; tags and releases; stashing and reverting; remotes; GitHub issues, pull requests and code review; branching strategies — feature branch, Git Flow and trunk-based; protected branches; GitHub Actions basics, workflow files, triggers and runners.
- Cloud Fundamentals & AWS Global Infrastructure
The history and economics of cloud computing; on-premises versus cloud cost models; capital versus operational expenditure; the essential characteristics — on-demand self-service, elasticity, pooling and measured service; deployment models; IaaS, PaaS and SaaS with real examples; lock-in and common misconceptions; the AWS shared responsibility model; regions, availability zones, edge locations and local zones; region selection criteria; the Console, CLI and SDKs; account creation, root-account protection, billing dashboard, budgets, Cost Explorer and the free tier.
- AWS IAM & Account Security
Identity and access management concepts; root user versus IAM users; groups, roles and temporary credentials through STS; JSON policy structure — version, effect, action, resource and condition; managed, customer-managed and inline policies; policy evaluation logic and explicit deny; least-privilege design; permission boundaries; multi-factor authentication and enforcement; access keys, rotation and secure storage; IAM roles for EC2 and service-to-service access; cross-account basics; credential reports and IAM Access Analyzer; CloudTrail as the audit record; AWS Organizations and multi-account concepts.
- VPC, Subnetting & Cloud Network Design
VPC concepts and CIDR planning for growth; public and private subnets across availability zones; route tables and route propagation; internet gateway; NAT gateway versus NAT instance trade-offs; security groups versus network ACLs and stateful versus stateless filtering; Elastic IPs and elastic network interfaces; VPC peering and transit gateway; gateway and interface endpoints; DNS resolution inside a VPC; bastion and jump-box patterns; VPC flow logs.
- EC2 Compute & Web Server Hosting
Instance families, generations and right-sizing; Amazon Machine Images and building custom AMIs; instance lifecycle, key pairs and SSH access; user data and bootstrapping; launch templates and versions; EBS volume types, IOPS and throughput, snapshots, resizing and encryption; instance store; Elastic IP association; placement groups; purchasing options — on-demand, reserved, savings plans and spot; installing and configuring Nginx or Apache; deploying a web application; connecting through a bastion host; the instance metadata service; EC2 status checks and CloudWatch basics.
- Storage, Databases & the Data Layer
Object, block and file storage compared; S3 buckets, objects, keys and prefixes; storage classes and intelligent tiering; lifecycle policies and archival to Glacier; versioning, replication and object lock; static website hosting; presigned URLs; bucket policies, ACLs, encryption and public-access blocking; EFS shared file systems and mount targets; storage cost comparison; relational versus non-relational data models; Amazon RDS engines, multi-AZ deployments, read replicas, backups and snapshots; securely connecting an application to RDS; DynamoDB tables, partition and sort keys, capacity modes, secondary indexes and TTL.
- Scaling, Architecture & AWS Capstone
Vertical versus horizontal scaling; Elastic Load Balancing with Application and Network Load Balancers, listeners, rules, target groups and health checks; Auto Scaling groups, launch templates, dynamic, scheduled and predictive policies, cooldowns and lifecycle hooks; high availability and fault tolerance across availability zones; Route 53 hosted zones, record types and routing policies; CloudWatch metrics, custom metrics, alarms, logs and dashboards; the AWS Well-Architected Framework; multi-tier reference architecture; cost optimisation fundamentals; load testing, troubleshooting and architecture review.
Useful for: Every cloud role. Cloud Support & Operations and Cloud Infrastructure Engineering are job-ready after this stage.
Cloud Computing Is Powering the Next Generation of Industry Leaders
- Live client work from week one, supervised by a trainer, not slides, not simulations.
- Cloud Engineer roles in Punjab start around ₹22,000 – ₹40,000 a month for a fresher with a working portfolio.
Reviewed by mentors. Built for interviews.Who can dothis course
The Cloud Computing programme is built for people at six different starting points, and the batch is deliberately mixed. What matters far more than your background is turning up consistently and finishing what each module asks you to build.
Students after 12th
Join from any stream. You start from fundamentals with no assumed knowledge, and most students run the programme alongside a degree at a Jalandhar college using the weekday or weekend batch.
Graduates and final-year students
If you are finishing a BA, BBA, B.Com, BCA or B.Tech, this is the shortest route from degree to salary. Enter placement season with project work in hand instead of a blank CV.
Working professionals
The weekend batch exists for people already earning. Career switchers typically become interview-ready for Cloud Engineer roles within five to six months without leaving their current job.
Business owners and freelancers
Owners take this programme to stop outsourcing work they cannot judge. Freelancers take it to bill clients beyond Punjab, since location does not limit remote work in this field.
Career restarters
A gap on the CV counts for less than work you can point at. The programme starts at zero and finishes with a portfolio and a documented internship letter, which is what an interviewer asks about after a break.
Self-taught learners
If free videos left you with notes but nothing built, what changes here is a trainer who reviews what you produced this week and a deadline attached to every module.
One course.A mesh of real tools.
Everything below is installed on the lab machines and used on live client work, not shown once in a slide and forgotten.
 GitHub
- Linux
- The operating system almost every cloud server runs on
- Bash
- Scripting on the Linux command line to automate routine server tasks
- Git
- Tracks every change to your code and infrastructure files
- GitHub
- Hosts your repositories, pull requests and portfolio for employers to see
- GitHub Actions
- Pipelines that run automatically inside a GitHub repository
- AWS
- Amazon Web Services, the cloud platform every lab runs on
- Amazon EC2
- Virtual servers you rent by the hour to run applications
- Amazon S3
- Storage for files, backups and static websites
- Amazon RDS
- Managed relational databases such as MySQL and PostgreSQL
- DynamoDB
- AWS's fast, managed NoSQL database
- Amazon VPC
- Your own private, secured network inside AWS
- AWS IAM
- Controls who can access what in an AWS account
- CloudWatch
- Metrics, logs and alarms for your AWS resources
- CloudFormation
- AWS's own tool for creating infrastructure from template files
- AWS Lambda
- Runs code on demand without a server to manage
- Route 53
- AWS's DNS service that points domain names at your applications
- Docker
- Packages an application and its dependencies into a portable container
- Kubernetes
- Runs and manages many containers, with scaling and self-healing
- Amazon EKS
- AWS's managed Kubernetes service
- Helm
- Packages Kubernetes applications into reusable charts
- Jenkins
- Automation server that runs build, test and deploy pipelines
- Terraform
- Creates cloud infrastructure from code instead of manual clicks
- Ansible
- Configures servers automatically and consistently
- SonarQube
- Checks code quality and blocks weak code in the pipeline
- Prometheus
- Collects live metrics from servers and applications
- Grafana
- Turns metrics into dashboards and alerts
- Elasticsearch
- Stores and searches logs as part of the ELK stack
- Amazon Bedrock
- Access to large AI models on AWS for building AI applications
- SageMaker
- AWS's service for training and hosting machine-learning models
- Python
- Programming language used to call AWS services and package AI apps
- FastAPI
- Python framework for serving a model or service as an API
- Streamlit
- Quick way to build a simple web interface for an AI app
- Wireshark
- Captures network traffic so you can see what is really happening
- NGINX
- Web server and reverse proxy in front of your applications
Get Certified in
Cloud Computing
Complete the course with a portfolio of live projects and receive an industry-recognised certificate, plus a documented internship letter accepted by Punjab universities.
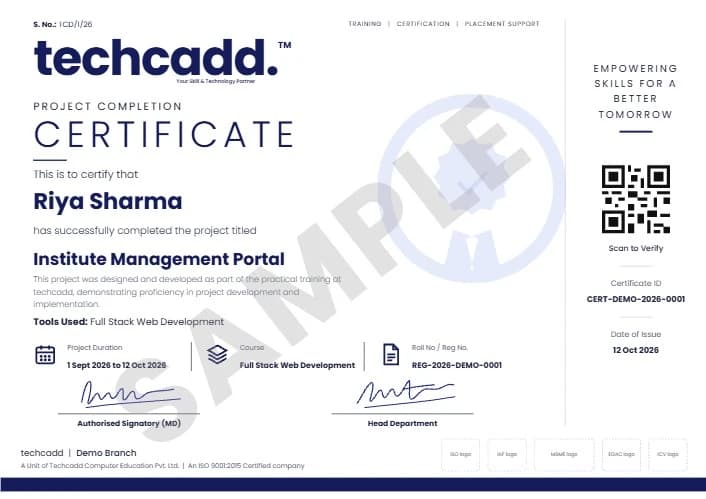
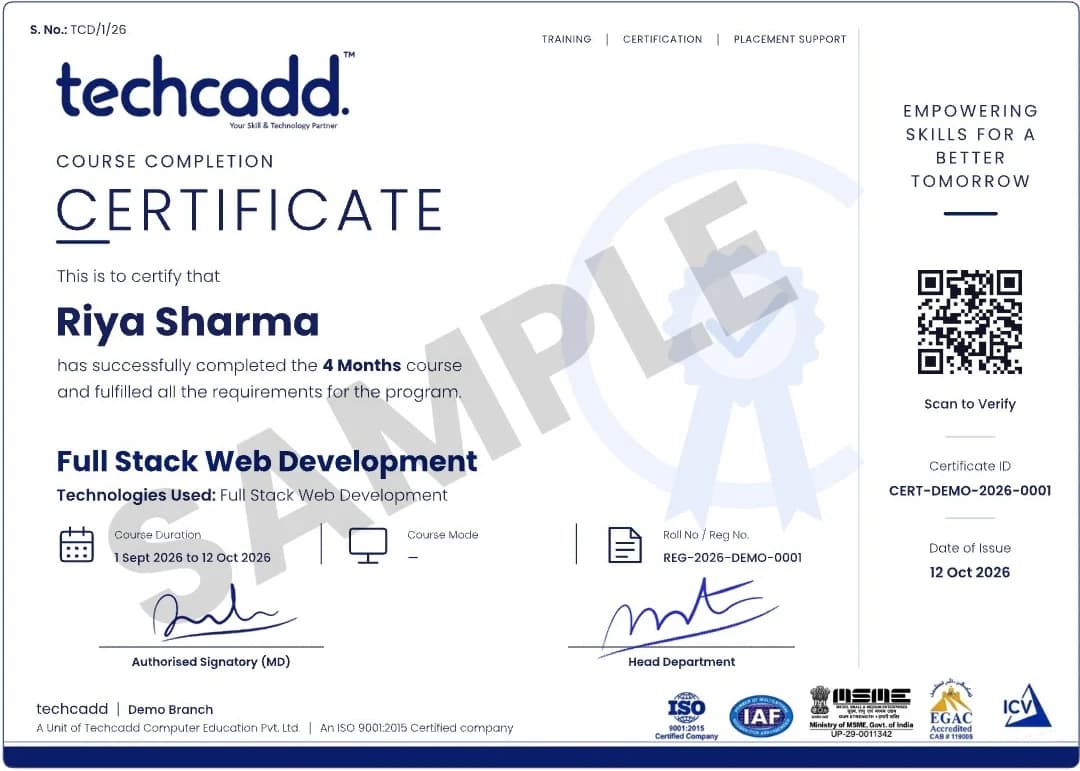
Two certificates on completion — the course certificate and a separate capstone project certificate.
Where this coursetakes you
The roles this opens, what they pay in Punjab and beyond, and who is hiring for them — the same figures our free Salary Estimator publishes, not a brochure number.
Cloud / DevOps Engineer
Manages cloud infrastructure, CI/CD pipelines, and container orchestration.
- Starting package
- ₹2.8–5LPA
- After 2 years
- ₹5.5–10LPA
Indicative ranges for Cloud / DevOps Engineer roles, compiled from public job-market listings and drawn on the same scale in every market. Actual offers vary by employer, skillset and interview performance — Punjab pay typically reaches 2× the fresher ceiling within two years of delivery experience.
Open the salary estimatorWhere Cloud / DevOps Engineer graduates get hired
- Cloud service providers and partners
- IT services companies with cloud practices
- Startup infrastructure and platform teams
- Remote DevOps and SRE contracts
What job roles open up after Cloud Computing?
Cloud skills sit under support, infrastructure, DevOps and AI work, so the roles you can apply for depend on how far up the ladder you go. They fall into two groups:
- Cloud Support Engineer (3-month track)
- Cloud Operations Associate (3-month track)
- Cloud Engineer / AWS Cloud Engineer (6-month track)
- DevOps Engineer (6-month track)
- Cloud Automation Engineer (9-month track)
- Multi-cloud Engineer (with Microsoft Azure course)
- Cloud Security Analyst (with Cybersecurity course)
- MLOps Engineer (with Machine Learning course)
- Site Reliability Engineer (with experience)
- Cloud Solutions Architect (with experience)
What does a Cloud Support Engineer or trainee interview test?
The entry-level role Stage 1 prepares you for, at three months. It tests whether you can administer Linux, script routine tasks, reason about networks and configure AWS IAM, VPC and EC2. What you show them: the Linux and Bash toolkit, the networking practical and your first AWS deployment.
What does a Cloud Engineer interview test?
The early-career role reached between three and six months. It tests whether you can deploy AWS workloads with storage, databases, scaling, monitoring and a secure multi-tier architecture. What you show them: the EC2, S3 and RDS application, the ALB and Auto Scaling build, and CloudWatch dashboards.
What does a DevOps Engineer interview test?
The early-career DevOps route, reached at six months. It tests whether you can containerise applications and automate delivery with Jenkins, Docker, Kubernetes and Terraform. What you show them: the CI/CD pipeline, the Kubernetes application and the infrastructure-as-code repository.
What does a Cloud Automation Engineer interview test?
The advanced role reached between six and nine months. It tests whether you can combine infrastructure automation, monitoring, security and operational workflow into one repeatable delivery system. What you show them: the modular Terraform estate, the CI/CD pipeline, the observability stack and the security report.
What does an AWS or Cloud DevOps Engineer interview test at senior level?
The expert-track role at nine months. It tests whether you can review architectures, harden AWS estates, run production Kubernetes, control cost and lead a full MLOps capstone. What you show them: the architecture review pack, the MLOps deployment and the expert capstone.
What job roles open up after Cloud Computing?
Graduates move into Cloud Engineer, DevOps Engineer, System Administrator, Cloud Support Associate and similar roles. Cloud and DevOps skills are the clearest salary jump available to a working IT professional in Punjab.
What can I earn, and how fast does it grow?
A fresher with a working portfolio starts around ₹22,000 – ₹40,000 a month in the Jalandhar market. With two years of delivery experience that typically doubles, and specialists who keep learning move well beyond it.
Can I freelance or work remotely with this skill?
Yes. A Jalandhar address costs you nothing on a remote brief. Students bill clients in Delhi, Dubai and Canada. The programme covers client handling, proposals and reporting so you can price and defend your work, not just do it.
Which industries hire for this in Punjab?
Beyond IT companies, the export houses, sports goods and hand tool manufacturers, immigration consultancies, hospitals, schools and real estate firms across Jalandhar all now hire for these skills directly.
Can I continue to higher studies or a specialisation later?
The certificate and portfolio stand on their own, and they stack. Most students move on to an adjacent techcadd track. The tools overlap, so the second programme is faster than the first.
Your Cloud Computing careerroadmap
The Cloud Computing programme is itself a ladder: each track continues where the last one ends. For most cloud and DevOps roles it is enough on its own; for a few specialisations you add one focused course. Here is how each path looks:
| Goal | Step 1 | Step 2 | Where you arrive |
|---|---|---|---|
| Cloud Support Engineer | Cloud Computing Certificate Program | Ready to apply (3-month Practitioner track) | Cloud Support Engineer, Cloud Operations Associate |
| Cloud / DevOps Engineer | Cloud Computing Certificate Program | Ready to apply (6-month Professional track) | Cloud Engineer, DevOps Engineer |
| Senior Cloud / Automation roles | Cloud Computing Certificate Program | Ready to apply (9-month Expert track) | Cloud Automation Engineer, AWS DevOps Engineer |
| Multi-cloud Engineer | Cloud Computing Certificate Program | Microsoft Azure | Cloud Engineer (AWS + Azure) |
| Cloud Security | Cloud Computing Certificate Program | Cybersecurity → SOC Analyst | Cloud Security Analyst |
| MLOps Engineer | Cloud Computing Certificate Program | MLOps Engineer |
Hands-on projectsyou will ship
Linux & Bash Automation Toolkit
Backup, log-parsing and health-check scripts scheduled with cron and version-controlled in Git.
Field: Cloud Support & Operations, Linux Automation
Secure AWS Network
A multi-AZ VPC with public and private subnets, NAT gateway, bastion access and flow logs.
Field: Cloud Infrastructure, Cloud Networking
AWS Web Application
An EC2, VPC, S3 and RDS deployment with Route 53 DNS and CloudWatch monitoring.
Field: Cloud Infrastructure Engineering
Scalable Cloud Architecture
A multi-tier architecture using ALB, Auto Scaling, private subnets and security controls.
Field: Cloud Infrastructure, Solutions Architecture
Event-Driven Serverless Workflow
Lambda, EventBridge, SNS and SQS defined and deployed through CloudFormation.
Field: Serverless AWS, Infrastructure as Code
AI Cloud Chatbot
An AI-powered chatbot built on Amazon Bedrock with Python, Streamlit and S3 storage.
Field: Cloud AI Services
Containerized Application
A Dockerised application packaged with Compose and deployed onto Kubernetes with Helm.
Field: Containers & Kubernetes
Automated CI/CD Pipeline
A GitHub-to-Jenkins pipeline with quality gates, image scanning and Kubernetes deployment.
Field: DevOps & CI/CD
Infrastructure as Code
A reusable Terraform configuration for AWS infrastructure with remote state and locking.
Field: DevOps, Infrastructure as Code
Cloud Operations Platform
An observable environment with SLO dashboards, log aggregation, alert routing and a postmortem.
Field: Site Reliability & Observability
Security & Recovery Review
A hardened AWS estate with least-privilege policies, an audit trail and a tested recovery runbook.
Field: Cloud Security
MLOps Deployment
A containerised AI service released through CI/CD with a model registry and drift monitoring.
Field: MLOps, Containers & Kubernetes
Learn it. Build it. Make it yours.
Every project moves through the same loop: understand the brief, build with guidance, then explain the decisions behind your work.
Understand
Break a real requirement into a clear plan and the right tools.
Linux & Bash Automation ToolkitBuild
Work hands-on with trainer feedback while the decisions are still easy to change.
Secure AWS NetworkPresent
Turn the finished work into a portfolio story you can defend in an interview.
AWS Web ApplicationWhy students choosetechcadd
There are many places to learn this in Jalandhar and the brochure syllabus looks similar at all of them. What differs is who teaches, whether you ever touch real work, and whether anyone picks up the phone after you have paid. techcadd has trained students across Punjab since 2016 on the same model: small batches, working practitioners as trainers, client projects as coursework.
Trainers who still do the work
Your trainer is not a full-time lecturer. They deliver client projects for techcadd's services arm, so examples in class are current rather than a case study from five years ago.
Live projects, real consequences
You work on genuine client requirements under supervision. This is where a portfolio comes from, and it is the first thing an interviewer asks to see.
Small batches and open lab hours
Batches stay small enough that a trainer sees your screen daily. Lab time runs outside class hours and doubt sessions continue until the concept lands.
Internship letter and certificate
Every student finishes with an industry-recognised certificate and a documented internship on real work, accepted for university industrial training requirements.
A placement cell that persists
Mock interviews, CV reviews and drives with hiring partners across Jalandhar and Ludhiana, repeated after a rejection, not abandoned.
Since 2016, 25,000+ students
A decade of hiring relationships in Punjab is why a call from our placement cell gets answered and why local employers know what our certificate means.
How techcaddcompares
Cloud courses are easy to advertise and hard to deliver, because they cost the provider money to run. These are the eight things worth asking before you pay any institute, including this one.
| Feature | techcadd | Other institutes |
|---|---|---|
| Curriculum | Industry-aligned, updated regularly | Often outdated or generic |
| Learning style | 100% hands-on, project-based | Mostly theory-heavy |
| Trainers | Industry-experienced mentors who still deliver client work | Mixed experience levels |
| Real projects | Multiple real-world projects plus a capstone | Limited or simulated projects |
| Cloud accounts | You provision real AWS and Azure resources in your own account, with billing guardrails set up on day one | Screenshots and simulator walkthroughs |
| Placement support | Dedicated career and interview preparation | Often limited or absent |
| Batch flexibility | Weekday, evening, weekend and 1-on-1 options | Fixed schedules |
| Doubt support | Ongoing mentor and community support | Limited post-class support |
| Certification | Industry-recognised certificate plus a documented internship letter | Varies |
The right-hand column describes what is commonly offered in the market, not any particular institute. Ask any institute you are considering — this one included — to show you the work its students actually produced.
What our studentsin Jalandhar say
- Google
techcadd's placement cell kept calling me for drives until I was placed. That persistence mattered more than the certificate for Cloud Computing.
Rohit SharmaJunior Analyst · Phagwara GoogleI was switching careers and worried I would be behind. Half the Cloud Computing batch were doing the same thing, and nobody made me feel slow.
Simranjeet SinghFreelancer · Kapurthala GoogleI joined the Cloud Computing batch with almost no background and finished with a project I could actually show. The trainers correct your work daily rather than just moving to the next slide.
Anjali VermaCareer Switcher · Jalandhar Cantt Googletechcadd's placement cell kept calling me for drives until I was placed. That persistence mattered more than the certificate for Cloud Computing.
Rohit SharmaJunior Analyst · Phagwara GoogleI was switching careers and worried I would be behind. Half the Cloud Computing batch were doing the same thing, and nobody made me feel slow.
Simranjeet SinghFreelancer · Kapurthala GoogleI joined the Cloud Computing batch with almost no background and finished with a project I could actually show. The trainers correct your work daily rather than just moving to the next slide.
Anjali VermaCareer Switcher · Jalandhar Cantt
- Google
What made Cloud Computing click for me was the lab time. You can sit after class and someone will still explain it until you get it.
Gurpreet DhillonWorking Professional · Nakodar GoogleThe Cloud Computing programme got me interview-ready faster than I expected. My interviewer asked to see my project and that was the whole conversation.
Manpreet KaurFinal-Year Student · Hoshiarpur GoogleI travelled in for the weekend Cloud Computing batch and it was worth every trip. Small batch, real work, no time wasted on theory nobody uses.
Vikas ChopraWeekend Batch · Ludhiana GoogleWhat made Cloud Computing click for me was the lab time. You can sit after class and someone will still explain it until you get it.
Gurpreet DhillonWorking Professional · Nakodar GoogleThe Cloud Computing programme got me interview-ready faster than I expected. My interviewer asked to see my project and that was the whole conversation.
Manpreet KaurFinal-Year Student · Hoshiarpur GoogleI travelled in for the weekend Cloud Computing batch and it was worth every trip. Small batch, real work, no time wasted on theory nobody uses.
Vikas ChopraWeekend Batch · Ludhiana
Frequently Asked Questions
Cloud computing turns infrastructure into a service. Instead of buying and maintaining every server, storage system and network device yourself, you provision computing resources on demand, scale them when workloads change, secure them through policy, automate them as code, and pay only for what you use. Four properties define it: on-demand provisioning, scalability up and down with demand, pay-as-you-go pricing, and high availability built on distributed infrastructure.
With traditional infrastructure you manage the hardware: you buy servers, configure, deploy and maintain them, capacity is fixed, the investment is up front, and scaling means purchasing more machines. In the cloud you manage the resources: services are provisioned within minutes, scale to demand, are billed on usage, and arrive with availability and redundancy options built in. Traditional infrastructure is the better answer when you need complete control over dedicated hardware, have predictable workloads or face specific compliance requirements; the cloud wins when you need flexibility, rapid deployment and the ability to adapt as requirements change.
There are three exit points on one 25-module ladder: 3 months (Practitioner, Modules 1–10), 6 months (Professional, Modules 11–18) and 9 months (Expert, Modules 19–25). They are nested rather than parallel — the six-month track is those first ten modules plus eight professional ones covering DevOps, AI and automation, and the nine-month track is all eighteen plus a seven-module expert extension that deepens the same domains rather than replacing them.
No. Module 01 begins with Linux administration, and Bash scripting, networking and Git follow, all taught from the ground up, so the programme is open to career changers and graduates with no coding background. From Module 05 onward every session runs on live AWS.
Linux, Bash, Git and GitHub for the foundation; AWS IAM, VPC, EC2, S3, EBS, EFS, RDS, DynamoDB, ALB, Auto Scaling, Route 53 and CloudWatch for core infrastructure; Lambda, API Gateway, EventBridge, SNS, SQS, Step Functions and CloudFormation for serverless; KMS, Secrets Manager, ACM, WAF, Shield, GuardDuty and Security Hub for security; Docker, Amazon ECR, Kubernetes, EKS and Helm for containers; Jenkins, GitHub Actions, SonarQube, Trivy and Terraform for delivery; Prometheus, Grafana, Alertmanager, Loki and ELK for observability; and Amazon Bedrock, SageMaker, Rekognition, Textract, Comprehend, Polly, Transcribe, Lex and boto3 for AI services.
Twelve portfolio projects across the three stages. Stage 1 produces a Linux and Bash automation toolkit, a secure multi-AZ AWS network, an EC2-RDS-S3 web application and a scalable multi-tier architecture. Stage 2 adds an event-driven serverless workflow, an AI cloud chatbot on Bedrock, a containerised application on Kubernetes, an automated CI/CD pipeline and a Terraform infrastructure repository. Stage 3 adds a cloud operations platform with SLO dashboards, a security and recovery review, and an MLOps deployment.
Stage 1 prepares you for Cloud Support Engineer, AWS Cloud Trainee, Junior Cloud Engineer and Cloud Operations Associate. Stage 2 prepares you for Cloud Engineer, AWS Cloud Engineer, DevOps Engineer and Cloud/DevOps Associate. Stage 3 prepares you for Senior Cloud/DevOps Engineer, Cloud Automation Engineer, AWS DevOps Engineer and Cloud Solutions Architect Associate. Every one of those interviews asks for work you have actually built, which is why each module ends in a graded artefact.
Cloud teams need people who can move from Linux, scripting and networking fundamentals through AWS infrastructure, deployment, security, containers, automation, monitoring and production troubleshooting — and prove it with work they have actually built. The most valuable skill in the field is knowing which service and architecture a problem actually needs: not every application requires Kubernetes, multiple servers or a complex architecture, and a simple application may only need a virtual machine, storage, a database and proper networking.
techcadd runs Cloud Computing over 3 to 6 months depending on the track you choose. Weekday, evening and weekend batches cover the same syllabus, and 1-on-1 training is available if you would rather set your own pace. Every class runs for 2 hours, whichever format you choose.
Fees depend on the course length and subject. techcadd counsellors share the exact fee for the length you choose and EMI options on request, and a demo class is free.
Students after 12th, graduates and final-year students, working professionals switching careers, and business owners all join this programme. You start from fundamentals, so a technical background helps but is not required.
Graduates typically move into roles such as Cloud Engineer, DevOps Engineer, System Administrator or Cloud Support Associate. Cloud and DevOps skills are the clearest salary jump available to a working IT professional in Punjab.
A fresher with a working portfolio typically starts around ₹22,000 – ₹40,000 per month in the Jalandhar market, rising substantially within two years of experience. Freelancers handling multiple clients often earn more, since remote work is not limited by location.
No training provider can honestly guarantee a job, and you should be cautious of anyone in Jalandhar who claims one. techcadd guarantees placement support: CV reviews, mock interviews, portfolio preparation and repeated drives with hiring partners across Jalandhar and Ludhiana.
You will work hands-on with AWS, Azure, Docker, Kubernetes, Terraform, Jenkins and the supporting toolchain used on live projects. All practice happens in the lab on licensed software, not on demo screenshots.
Yes. Every student receives an industry-recognised certificate on completion plus a documented internship letter based on live client work. The internship satisfies the industrial training requirement at most Punjab universities.
Every module ends with something you built. This programme finishes with a live project drawn from techcadd's own client delivery work, supervised by a trainer, which becomes the portfolio you take to interviews.
Yes. techcadd Jalandhar runs weekday, evening and weekend batches in parallel so working professionals and college students can both attend, and 1-on-1 training is available for a fully personal schedule. Every class (batch or 1-on-1) runs for 2 hours; book a free demo class to see the lab and meet the trainer before enrolling.
Both, in a sense. It teaches general cloud and DevOps skills (Linux, networking, Git, containers, CI/CD, Terraform, monitoring) and uses AWS as the cloud platform for every hands-on lab. That combination is what most Cloud Engineer and DevOps listings ask for.
Those are shorter courses that each focus on one area. This programme joins them into one ladder that starts from Linux and networking and climbs through AWS, security, containers, CI/CD, AI services and MLOps. Choose a single course if you already have the foundation and need one skill; choose this if you want the whole path.
No. The AI modules teach you to use managed AI services such as Amazon Bedrock and to deploy and monitor models in production, which is the cloud and MLOps side of AI. Building and training models is taught in techcadd's Machine Learning and Data Science courses.
It is enough for entry-level cloud support and junior cloud roles, because it covers Linux, networking, Git and core AWS and ends in a multi-tier AWS capstone. Most DevOps Engineer listings also ask for Docker, Kubernetes, CI/CD and Terraform, which start in the 6-month track.
No. Many cloud jobs never touch Kubernetes, and a simple application may only need a server, storage and a database. Kubernetes matters for DevOps and platform roles in larger teams, which is why it is taught in Stage 2 rather than at the start.
Choose the rightduration for you
Modules are numbered 01 to 25 in a single sequence, and progression is capability-gated: you advance when a deliverable passes review, not when the calendar says so. Every module is specified the same way — the topics in teaching order, the named platforms and tools used in labs, the production problem the skill solves, and a practical artefact for your portfolio.
Practitioner
Modules 1 – 10
Build the operating-system, networking, version-control and AWS foundation needed to deploy real workloads. Prepares you for Cloud Support Engineer, AWS Cloud Trainee, Junior Cloud Engineer and Cloud Operations Associate roles.
Professional
Modules 11 – 18
Continue into serverless AWS, cloud security, AI services, containers, Kubernetes, CI/CD, Terraform, monitoring and MLOps. Prepares you for Cloud Engineer, AWS Cloud Engineer, DevOps Engineer and Cloud/DevOps Associate roles.
Expert
Modules 19 – 25
Deepen the same cloud, AWS, DevOps and AI domains into architecture, security, automation, reliability and operational mastery. Prepares you for Senior Cloud/DevOps Engineer, Cloud Automation Engineer, AWS DevOps Engineer and Cloud Solutions Architect Associate roles.
| Module | 3 Months | 6 Months | 9 Months |
|---|---|---|---|
| 01Linux Administration & File SystemsLinux architecture, kernel, shell and user space; distributions and release models; installation on virtual machines and cloud instances; the file system hierarchy, links and inodes; core commands for navigation, search, archiving and compression; redirection, pipes and filters with grep, awk and sed; users, groups, ownership, permissions, umask, sudo and access control lists; package management with apt, yum and dnf; processes, services and unit files under systemd; disks, partitions, mounting, /etc/fstab and swap; SSH key-based authentication; cron and scheduled jobs; log locations, journalctl and first-line troubleshooting. Tools: Linux (Ubuntu / Amazon Linux), Bash, SSH, systemd, cron. Deliverable: a Linux administration lab covering users, permissions, services, mounts and SSH, plus a personal command reference sheet. | Included | Included | Included |
| 02Bash Scripting & Server AutomationShell scripting fundamentals; the shebang, execution permissions and PATH; variables, quoting, expansion and command substitution; positional parameters and argument parsing; standard input, output and error; exit codes; conditionals and loops; functions, scope and return values; arrays; text-processing pipelines for log analysis; here-documents; error handling with set -euo pipefail and trap; debugging with set -x; backup, log-rotation, user-provisioning and health-check scripts; scheduling with cron and systemd timers. Tools: Bash, cron, rsync, tar, grep/awk/sed, Git. Deliverable: a Bash automation project — backup script, log parser and server health-check suite — with usage documentation. | Included | Included | Included |
| 03Computer Networking & ProtocolsLAN, WAN, MAN and PAN; topologies; routers, switches, firewalls and gateways; the OSI and TCP/IP models layer by layer; encapsulation and framing; IPv4 and IPv6 addressing, CIDR notation and hands-on subnetting; MAC addressing and ARP; DNS hierarchy, resolution and record types; DHCP; NAT and port address translation; static and dynamic routing; TCP versus UDP, the three-way handshake and common service ports; HTTP, HTTPS and TLS basics; VPN types; troubleshooting with ping, traceroute, dig, netstat, ss, curl and tcpdump. Tools: ip/ifconfig, ping, traceroute, dig, curl, tcpdump, Wireshark. Deliverable: a networking practical, a subnetting exercise set and a documented connectivity troubleshooting report. | Included | Included | Included |
| 04Git, GitHub & Version Control WorkflowVersion control concepts and why infrastructure belongs in it; repositories, the staging area and the commit graph; inspecting history with log, diff and blame; branching, merging, rebasing and conflict resolution; .gitignore and repository hygiene; tags and releases; stashing and reverting; remotes; GitHub issues, pull requests and code review; branching strategies — feature branch, Git Flow and trunk-based; protected branches; GitHub Actions basics, workflow files, triggers and runners. Tools: Git, GitHub, GitHub Actions. Deliverable: a team repository with a documented branching strategy, reviewed pull requests and a first GitHub Actions workflow. | Included | Included | Included |
| 05Cloud Fundamentals & AWS Global InfrastructureThe history and economics of cloud computing; on-premises versus cloud cost models; capital versus operational expenditure; the essential characteristics — on-demand self-service, elasticity, pooling and measured service; deployment models; IaaS, PaaS and SaaS with real examples; lock-in and common misconceptions; the AWS shared responsibility model; regions, availability zones, edge locations and local zones; region selection criteria; the Console, CLI and SDKs; account creation, root-account protection, billing dashboard, budgets, Cost Explorer and the free tier. Tools: AWS Management Console, AWS CLI, AWS Billing, Budgets and Cost Explorer. Deliverable: an AWS account setup lab, a region and service-model comparison note, and a billing alarm and budget configuration. | Included | Included | Included |
| 06AWS IAM & Account SecurityIdentity and access management concepts; root user versus IAM users; groups, roles and temporary credentials through STS; JSON policy structure — version, effect, action, resource and condition; managed, customer-managed and inline policies; policy evaluation logic and explicit deny; least-privilege design; permission boundaries; multi-factor authentication and enforcement; access keys, rotation and secure storage; IAM roles for EC2 and service-to-service access; cross-account basics; credential reports and IAM Access Analyzer; CloudTrail as the audit record; AWS Organizations and multi-account concepts. Tools: AWS IAM, STS, IAM Policy Simulator, AWS CLI, CloudTrail. Deliverable: an IAM baseline with groups, roles, MFA and a password policy, plus a custom least-privilege policy and a credential audit report. | Included | Included | Included |
| 07VPC, Subnetting & Cloud Network DesignVPC concepts and CIDR planning for growth; public and private subnets across availability zones; route tables and route propagation; internet gateway; NAT gateway versus NAT instance trade-offs; security groups versus network ACLs and stateful versus stateless filtering; Elastic IPs and elastic network interfaces; VPC peering and transit gateway; gateway and interface endpoints; DNS resolution inside a VPC; bastion and jump-box patterns; VPC flow logs. Tools: Amazon VPC, Security Groups, NACLs, NAT Gateway, VPC Endpoints, VPC Flow Logs. Deliverable: a multi-AZ VPC build with public and private subnets, NAT, bastion access, flow logs and a documented routing diagram. | Included | Included | Included |
| 08EC2 Compute & Web Server HostingInstance families, generations and right-sizing; Amazon Machine Images and building custom AMIs; instance lifecycle, key pairs and SSH access; user data and bootstrapping; launch templates and versions; EBS volume types, IOPS and throughput, snapshots, resizing and encryption; instance store; Elastic IP association; placement groups; purchasing options — on-demand, reserved, savings plans and spot; installing and configuring Nginx or Apache; deploying a web application; connecting through a bastion host; the instance metadata service; EC2 status checks and CloudWatch basics. Tools: Amazon EC2, EBS, AMI, Launch Templates, Nginx/Apache, SSH, CloudWatch. Deliverable: a hosted web application on EC2 with a custom AMI, launch template, encrypted EBS and a documented bootstrap script. | Included | Included | Included |
| 09Storage, Databases & the Data LayerObject, block and file storage compared; S3 buckets, objects, keys and prefixes; storage classes and intelligent tiering; lifecycle policies and archival to Glacier; versioning, replication and object lock; static website hosting; presigned URLs; bucket policies, ACLs, encryption and public-access blocking; EFS shared file systems and mount targets; storage cost comparison; relational versus non-relational data models; Amazon RDS engines, multi-AZ deployments, read replicas, backups and snapshots; securely connecting an application to RDS; DynamoDB tables, partition and sort keys, capacity modes, secondary indexes and TTL. Tools: Amazon S3, EBS, EFS, Amazon RDS, DynamoDB, AWS Backup. Deliverable: an S3 static site with a lifecycle policy, an RDS-backed application with secure connectivity, and a DynamoDB table design note. | Included | Included | Included |
| 10Scaling, Architecture & AWS CapstoneVertical versus horizontal scaling; Elastic Load Balancing with Application and Network Load Balancers, listeners, rules, target groups and health checks; Auto Scaling groups, launch templates, dynamic, scheduled and predictive policies, cooldowns and lifecycle hooks; high availability and fault tolerance across availability zones; Route 53 hosted zones, record types and routing policies; CloudWatch metrics, custom metrics, alarms, logs and dashboards; the AWS Well-Architected Framework; multi-tier reference architecture; cost optimisation fundamentals; load testing, troubleshooting and architecture review. Tools: ALB, Auto Scaling, Route 53, CloudWatch, EC2, VPC, S3, RDS. Deliverable: a complete AWS capstone — multi-tier, load-balanced and auto-scaled — with an architecture diagram, documentation and a mock interview. | Included | Included | Included |
| 11Advanced AWS & Serverless ArchitectureCloudWatch log groups, metric filters, composite alarms, Logs Insights and dashboards; CloudTrail trails, event history, log-file validation and multi-region trails; AWS Config rules and resource timelines; CloudFormation templates, stacks, parameters, mappings, conditions, outputs, nested stacks, change sets and drift detection; Route 53 advanced routing — weighted, latency, failover and geolocation with health checks; Lambda runtimes, handlers, layers, environment variables, memory and timeout tuning, concurrency and cold starts; API Gateway REST and HTTP APIs; EventBridge buses, rules and schedules; SNS topics and filtering; SQS standard and FIFO queues, visibility timeout and dead-letter queues; Step Functions state machines. Tools: Lambda, API Gateway, EventBridge, SNS, SQS, Step Functions, CloudFormation, CloudWatch, CloudTrail, Route 53. Deliverable: a CloudFormation infrastructure-as-code stack, an event-driven serverless workflow, and a CloudWatch dashboard with alarms. | Not included | Included | Included |
| 12Cloud Security, Encryption & Disaster RecoverySecurity under the shared responsibility model; IAM hardening and least privilege at scale; encryption at rest and in transit; KMS customer-managed keys, key policies, grants, rotation and envelope encryption; Secrets Manager and Systems Manager Parameter Store; certificate issuance and renewal with ACM; WAF rules, managed rule groups and rate limiting; Shield and DDoS resilience; GuardDuty findings and Security Hub standards; VPC security review and least-exposure design; backup strategy with AWS Backup, snapshots, retention and vault lock; recovery point and recovery time objectives; disaster-recovery patterns — backup and restore, pilot light, warm standby and multi-site; recovery testing and written runbooks. Tools: IAM, KMS, Secrets Manager, Parameter Store, ACM, WAF, Shield, GuardDuty, AWS Backup. Deliverable: a security hardening checklist applied to a live environment, an encryption and secrets implementation, and a tested DR runbook. | Not included | Included | Included |
| 13AI, Machine Learning & Generative AI FoundationsArtificial intelligence, machine learning and deep learning distinguished; supervised, unsupervised and reinforcement learning; the model lifecycle from data and features through training and validation to inference; neural networks, layers, weights, activation functions and backpropagation in concept; overfitting, bias-variance and evaluation metrics; generative AI and foundation models; large language models, tokens, context windows, temperature and embeddings; vector databases and retrieval-augmented generation; prompt-engineering patterns; popular model families and how to choose between them; responsible AI, bias, hallucination, privacy and data governance; AI security concerns including prompt injection; the infrastructure demands of AI workloads. Tools: Python, Jupyter/Colab, NumPy and pandas basics, prompt tooling, vector-store concepts. Deliverable: an AI concepts assessment, a prompt-engineering workbook, and a short written model-selection and evaluation note. | Not included | Included | Included |
| 14AWS AI Services & Bedrock ApplicationsThe AWS AI and machine-learning service stack; Amazon Bedrock — model access, invocation parameters, streaming, knowledge bases and guardrails; Rekognition for image and video analysis; Textract for document and form extraction; Comprehend for entity, sentiment and key-phrase analysis; Polly for speech synthesis; Transcribe for speech-to-text; Translate for language conversion; Lex for conversational interfaces; a SageMaker overview covering notebooks, training jobs and hosted endpoints; calling AI services from Python with boto3; building an interface with Streamlit; storing prompts, documents and artefacts in S3; IAM permissions for AI services; quota, latency and cost considerations. Tools: Amazon Bedrock, Rekognition, Textract, Comprehend, Polly, Translate, Transcribe, Lex, SageMaker, Python (boto3), Streamlit, S3. Deliverable: an AI-powered cloud chatbot built on Bedrock, Python, Streamlit and S3, with documented prompts, guardrails and cost notes. | Not included | Included | Included |
| 15Docker & ContainerizationContainers versus virtual machines; Docker architecture — daemon, client and registry; images, layers and the union file system; writing Dockerfiles with FROM, RUN, COPY, ENV, ARG, EXPOSE, ENTRYPOINT and CMD; build context, layer caching and .dockerignore; multi-stage builds and minimal base images; tagging, versioning and image promotion; running, inspecting, exec-ing into and debugging containers; port publishing; volumes and bind mounts; Docker networks; environment variables and secret handling; Docker Compose for multi-container stacks with dependencies and healthchecks; registries with Docker Hub and Amazon ECR; image size reduction and vulnerability scanning; container logging and resource limits. Tools: Docker, Dockerfile, Docker Compose, Docker Hub, Amazon ECR, Trivy. Deliverable: a containerised multi-service application with an optimised multi-stage Dockerfile, a Compose stack and a published image. | Not included | Included | Included |
| 16Kubernetes Orchestration & HelmWhy orchestration is needed; Kubernetes architecture — API server, etcd, scheduler, controller manager, kubelet and kube-proxy; clusters, nodes and the declarative model; Pods, ReplicaSets and Deployments; rolling updates, revision history and rollbacks; Services (ClusterIP, NodePort, LoadBalancer) and Ingress controllers; ConfigMaps and Secrets; namespaces, labels, selectors and annotations; resource requests, limits and quality of service; liveness, readiness and startup probes; persistent volumes, claims and storage classes; StatefulSets, DaemonSets and Jobs; the Horizontal Pod Autoscaler; Helm charts, templates, values, dependencies and releases; managed Kubernetes on AWS (EKS); a kubectl troubleshooting workflow. Tools: Kubernetes, kubectl, Minikube/kind, Amazon EKS, Helm. Deliverable: a Kubernetes deployment with services, ingress, config, secrets and autoscaling, packaged as a versioned Helm chart. | Not included | Included | Included |
| 17CI/CD Pipelines & Infrastructure as CodeContinuous integration, delivery and deployment distinguished; Jenkins installation, plugins, credentials, agents and shared libraries; freestyle versus pipeline jobs; declarative Jenkinsfile syntax — stages, steps, environment, parallel and post conditions; GitHub integration, webhooks and multibranch pipelines; automated testing inside the pipeline; static code analysis and quality gates with SonarQube; container image scanning with Trivy; building, tagging and pushing Docker images; deploying to Kubernetes from a pipeline; approval gates, artefact promotion and rollback; GitHub Actions as an alternative runner; Terraform fundamentals — providers, resources, variables, locals, outputs and data sources; the init-plan-apply workflow; state files, remote state on S3 and DynamoDB locking; modules, reuse and versioning; workspaces; drift management. Tools: Jenkins, GitHub, GitHub Actions, SonarQube, Trivy, Docker, Kubernetes, Terraform. Deliverable: an end-to-end CI/CD pipeline from commit to Kubernetes deployment, plus a Terraform-managed AWS environment with remote state. | Not included | Included | Included |
| 18Monitoring, Observability & MLOps DeploymentMonitoring versus observability; the three signals — metrics, logs and traces; Prometheus architecture, scrape configuration, exporters and PromQL; Node Exporter and application instrumentation; Grafana data sources, dashboards, panels, variables and annotations; Alertmanager routing, grouping, inhibition and notification channels; log aggregation with Loki and with the ELK stack; CloudWatch integration and cross-source dashboards; designing alerts that are actionable; the MLOps lifecycle; experiment tracking, model registry and versioning; packaging a model behind FastAPI; building interfaces with Streamlit; dockerising AI applications; deploying models to EC2; CI/CD for AI applications; model performance monitoring and drift detection. Tools: Prometheus, Node Exporter, Grafana, Alertmanager, Loki, ELK, FastAPI, Streamlit, Docker, AWS EC2, Jenkins, GitHub Actions. Deliverable: an end-to-end AI cloud project with monitoring dashboards, alert routing, CI/CD and a final industry presentation. | Not included | Included | Included |
| 19Cloud Architecture & Resilience EngineeringArchitecting from stated requirements — availability, latency, durability, security and cost targets; applying the Well-Architected Framework as a review discipline; multi-AZ and multi-region patterns; active-active versus active-passive; stateless application design and session handling; caching layers with CloudFront and ElastiCache; decoupling with queues, topics and events; database scaling patterns — read replicas, caching, partitioning and connection pooling; failure-mode and effects analysis; blast-radius reduction and bulkheads; chaos experiments and game-day exercises; capacity planning and load modelling; writing reference architectures and architecture decision records. Tools: AWS VPC, ALB, Auto Scaling, Route 53, CloudFront, ElastiCache, CloudWatch, Well-Architected Tool. Deliverable: a reference architecture pack, a failure-mode analysis, a game-day exercise report and a set of architecture decision records. | Not included | Not included | Included |
| 20AWS Security Engineering & ComplianceIdentity federation and single sign-on; multi-account strategy with AWS Organizations, organisational units and service control policies; least-privilege policy authoring, review and testing; permission boundaries and role chaining; KMS key hierarchy, grants, cross-account and cross-region encryption; Secrets Manager rotation functions; certificate lifecycle management; WAF rule tuning, rate limits and bot control; Shield Advanced concepts; GuardDuty finding triage and automated response; Security Hub standards and CIS benchmark scoring; VPC flow log analysis; CloudTrail-based investigation and timeline reconstruction; incident-response runbooks and escalation; backup validation, restore drills and cross-region recovery; producing compliance evidence and audit trails. Tools: IAM, AWS Organizations, KMS, Secrets Manager, WAF, Shield, GuardDuty, Security Hub, CloudTrail, AWS Backup. Deliverable: a security hardening report, a CloudTrail investigation exercise and a tested cross-region recovery runbook. | Not included | Not included | Included |
| 21Cloud AI Services EngineeringDesigning applications around managed AI services; Bedrock integration patterns, model selection and parameter tuning; prompt templates, system prompts, guardrails and output validation; embeddings, vector stores and retrieval-augmented generation on AWS; knowledge bases and document ingestion pipelines with Textract and S3; Rekognition and Comprehend inside processing pipelines; Polly, Transcribe and Translate in media workflows; Lex conversational flows and fulfilment with Lambda; SageMaker endpoints, batch transform and inference options; cost, latency, throttling and quota management; evaluation harnesses, regression tests and human review for AI features; privacy, data residency and responsible-AI controls. Tools: Amazon Bedrock, SageMaker, Rekognition, Textract, Comprehend, Polly, Translate, Transcribe, Lex, Lambda, Python (boto3), S3. Deliverable: a production-style AI service integration with documented architecture, evaluation test cases and a cost analysis. | Not included | Not included | Included |
| 22Production Containers & Kubernetes OperationsContainer image strategy, base-image selection and hardening; multi-stage build optimisation and scanning inside the pipeline; registry lifecycle and immutability policies; Kubernetes cluster operations on EKS — node groups, IAM roles for service accounts and cluster upgrades; namespace and RBAC design; resource quotas and limit ranges; probes, PodDisruptionBudgets and graceful shutdown; horizontal pod and cluster autoscaling; ingress controllers, TLS termination and DNS integration; external secrets integration; rolling, blue-green and canary deployment strategies; troubleshooting CrashLoopBackOff, ImagePullBackOff, OOMKills, pending pods and service networking failures. Tools: Docker, Amazon ECR, Kubernetes, Amazon EKS, Helm, kubectl, Trivy. Deliverable: a hardened Kubernetes application with RBAC, quotas, a canary rollout and a documented troubleshooting playbook. | Not included | Not included | Included |
| 23Infrastructure Automation & GitOps DeliveryTerraform at scale — module design, composition, versioning and private registries; environment separation with workspaces and directory layouts; remote state, locking, imports and state manipulation; data sources, dynamic blocks, for_each and lifecycle rules; policy as code and automated plan review; handling secrets safely in infrastructure code; Ansible fundamentals for configuration management; designing pipelines for infrastructure change with plan, review and approval stages; GitOps principles and pull-request-driven delivery; drift detection and reconciliation; rollback and change-management procedure; documenting an estate for handover. Tools: Terraform, Terraform modules, Ansible, Git/GitHub, Jenkins, GitHub Actions. Deliverable: a modular multi-environment Terraform repository, an infrastructure CI/CD pipeline and a documented rollback procedure. | Not included | Not included | Included |
| 24Site Reliability, Observability & Cost OptimisationSite reliability engineering principles; service level indicators, objectives, agreements and error budgets; toil identification and reduction; instrumenting applications for metrics and structured logs; distributed tracing concepts; Prometheus at scale with recording rules, relabelling and federation; Grafana dashboard design for operators rather than for screenshots; Alertmanager routing, silencing, escalation and on-call rotation; runbooks, incident command and communication; blameless postmortems and follow-up tracking; load and performance testing; right-sizing compute and storage; savings plans, reserved capacity and spot strategy; storage lifecycle and data-transfer cost control; tagging, cost allocation and budgets; FinOps reporting to non-technical stakeholders. Tools: Prometheus, Grafana, Alertmanager, Loki, ELK, CloudWatch, AWS Cost Explorer, AWS Budgets, Compute Optimizer. Deliverable: an observability stack with SLO dashboards and alert routing, an incident postmortem, and a cost-optimisation report with measured savings. | Not included | Not included | Included |
| 25MLOps at Scale & Expert CapstoneProduction MLOps architecture; data and feature pipelines; experiment tracking, model registry and lineage; packaging models with FastAPI and containers; deployment strategies for models — batch, real-time and serverless inference; shadow deployment and A/B evaluation; automated retraining triggers; model monitoring, data quality and drift detection; CI/CD for AI applications including dependency and image scanning; expert capstone planning and scoping; integrating infrastructure, application, AI, security, automation and observability into one coherent system; architecture presentation and defence; project documentation, technical viva and final evaluation. Tools: FastAPI, Streamlit, Docker, Kubernetes, Terraform, Jenkins, Prometheus, Grafana, AWS (EC2, S3, ECR, SageMaker). Deliverable: the expert capstone with dashboards, CI/CD evidence, an architecture presentation, a technical viva and final evaluation. | Not included | Not included | Included |
Nested, not parallel. Three months is ten foundation modules ending in a multi-tier AWS capstone; six months is those same ten plus eight professional modules covering DevOps, AI and automation; nine months is all eighteen plus a seven-module expert extension that deepens the existing domains rather than replacing them. Nothing is removed when a learner extends.
Not sure which cloud career path is right for you?
One call with a counsellor is usually enough to find out. Tell us what you enjoy and where you want to work, and we will show you which track to start on and whether to aim for support, cloud engineering, DevOps, security or MLOps. Book a free demo class and see the lab before you decide.
What you are reallybeing taught
Services get renamed and consoles get redesigned. These ideas do not — they are what you are really being taught, and what a strong candidate can articulate under questioning.
Build from fundamentals
Linux, scripting, networking and cloud concepts make every AWS service easier to reason about. The console is a shortcut over things you should already understand.
Automate repeatable work
Bash, GitHub Actions, Jenkins, Ansible and Terraform turn manual steps into controlled, reviewable workflows. Anything done twice by hand is a script that has not been written yet.
Design for failure
High availability, Auto Scaling, monitoring, backups and disaster recovery belong in the architecture, not in the postmortem.
Secure by default
IAM, MFA, least privilege, encryption, KMS, WAF and secrets management are part of engineering, not an afterthought bolted on before an audit.
Observe what you operate
Prometheus, Grafana, Loki, ELK, CloudWatch and Alertmanager make system behaviour visible before users report it.
Prove the result
Projects, practical labs, documentation, viva, mock interviews and final presentations turn learning into evidence somebody else can check.
Ask aboutCloud Computing
Send your question and a counsellor will call you back about batch timings, fees, EMI options, placement record, or whether this course fits your degree.
- Free counselling and demo class
- Weekday, evening, weekend or 1-on-1, all 2-hour classes
- Internship letter and placement support