Best SOC Analyst Course & Training in Jalandhar
Learn monitoring, triaging and responding to security incidents the way a live Security Operations Centre actually runs, taught on live client work at techcadd Jalandhar rather than from slides.
- Live client projects
- Practitioner trainers
- Placement support
- Certificate + internship
- Duration
- 3 Months
- Mode
- Classroom, Weekend & 1-on-1
- Eligibility
- 12th Pass Onward
- Students trained
- 25,000+Students trainedsince 2016
- Google rating
- 4.9★Google rating556+ reviews
- Practical training
- 100%Practical traininglive client work
Course overview
techcadd's Best SOC Analyst Course & Training in Jalandhar takes you from SOC fundamentals and the analyst's daily workflow to Capstone: a simulated incident, detected and written up, taught on Splunk, Wireshark, Microsoft Sentinel. You work on live client briefs under trainer supervision, not slideware. Every module ends in a portfolio deliverable you can show in an interview.
The people whocatch the attack
A Security Operations Centre (SOC) is the team that watches an organisation's computers, networks and accounts around the clock. A SOC analyst reads the alerts that security tools raise, decides which ones are real, and escalates or responds before an attack does damage. It is defensive work, and it is where most people start a cybersecurity career.
Think of the control room of a big shopping mall in Jalandhar: dozens of CCTV screens, most showing nothing unusual. The guard's skill is noticing the one screen that matters and acting quickly and calmly. A SOC analyst does the same with logs and alerts. This course trains you for that seat. Each field below shows how much of it the course covers.
- Job-ready focus2 fields
- The course trains you for entry-level work in this field.
- Strong foundation3 fields
- You learn the base skills here; one specialised course makes you job-ready.
- Introduced1 field
- You will use it in the course, but it is not a specialisation.
- Not covered1 field
- Not part of this course; available as a separate techcadd course.
What this course makes you job-ready for
Job-ready focusSOC Monitoring & Alert Triage
Working through the queue of alerts from a SIEM tool, separating real threats from false alarms, and escalating the real ones with clear notes.
An alert says a staff account logged in from two countries within ten minutes. You check the logs, confirm it is suspicious and escalate it to L2 with the evidence.
- SOC Analyst tools used
- SplunkMicrosoft SentinelMITRE ATT&CK framework
- Job roles
- SOC Analyst L1Security Monitoring Analyst
Foundations (SOC fundamentals and the analyst's daily workflow, SIEM tools and log analysis, incident detection, triage and escalation). Project: SOC Analyst Fundamentals Build.
Incident Response
Once an attack is confirmed, following a set plan (a playbook) to contain it, remove it and record what happened, so the business can recover.
After ransomware is detected on one laptop at an export house, isolating it from the network, checking whether others are affected and writing the incident report.
- SOC Analyst tools used
- Incident response playbooksSplunkCrowdStrike
- Job roles
- Incident Responder (junior)SOC Analyst L1/L2
Applied Work (incident response playbooks; capstone: a simulated incident, detected and written up). Project: Portfolio Capstone.
What this course lays the foundation for
Strong foundationEndpoint Detection & Response (EDR)
Monitoring and protecting individual devices such as laptops and servers, using tools that spot suspicious behaviour on the machine itself.
An EDR tool notices a spreadsheet starting a hidden program on an accountant's PC, and the analyst isolates the PC.
- SOC Analyst tools used
- CrowdStrikeEDR consoles
- Job roles
- SOC AnalystEDR Analyst
Core Skills (endpoint detection and response). Administering an EDR platform across a whole company is learned on the job.
Threat Intelligence
Collecting and using information about current attackers, such as known bad IP addresses, file fingerprints and attack techniques, so defenders know what to look for.
Checking whether an IP address seen in your logs appears on a public list of known malicious servers.
- SOC Analyst tools used
- MITRE ATT&CK frameworkthreat intelligence feeds
- Job roles
- Threat Intelligence Analyst (junior)SOC Analyst
Core Skills (threat intelligence and indicator of compromise basics). Dedicated threat intelligence roles usually follow SOC experience.
Network Traffic Analysis
Studying the traffic moving across a network to spot unusual patterns, such as a computer sending large amounts of data out at night.
Noticing in Wireshark that a reception PC is repeatedly contacting an unknown server every five minutes.
- SOC Analyst tools used
- Wireshark
- Job roles
- SOC AnalystNetwork Security Analyst
Core Skills (network traffic analysis for anomalies). Deeper networking is taught in techcadd's Network Security & CCNA course.
What this course introduces
IntroducedDigital Forensics
Investigating in depth after an incident: recovering evidence from disks, memory and phones in a way that holds up in legal or corporate proceedings.
Preparing evidence from a seized laptop for a bank's internal fraud inquiry.
- SOC Analyst tools used
- AutopsyFTK ImagerVolatility
- Job roles
- Digital Forensics Analyst
The incident write-up in the capstone is the first step. Forensic evidence handling is taught in techcadd's Cyber Forensics course.
Not part of this course
Not coveredEthical Hacking & Penetration Testing
The offensive side: testing systems with permission to find weaknesses before attackers do.
A tester finds a weak login page on a company website and reports how to fix it.
- SOC Analyst tools used
- Kali LinuxBurp SuiteMetasploit
- Job roles
- Penetration TesterEthical Hacker
Not part of this course. It is taught in techcadd's Ethical Hacking and Penetration Testing courses, and both sides are combined in the Cybersecurity programme.
Clearing up common confusions
What do L1 and L2 mean?
L1 analysts watch the alert queue and do first checks. L2 analysts take escalated cases and investigate them in depth. Freshers usually join as L1 and move to L2 with experience; this course prepares you for L1 and gives you the base for L2.
Is a SOC analyst a hacker?
No. A SOC analyst defends; a penetration tester attacks with permission. Both need to understand how attacks work, but the daily work is very different. SOC roles are also far more numerous, which makes them the usual first job in security.
SOC Analyst is also used in…
Cloud security monitoring, managed security service providers (MSSPs) that run SOCs for many clients, and compliance teams that need logs reviewed for audits. The alert-handling and investigation habits you build here carry straight across.
At a glance: what this course covers
| Field | Coverage in this course | Where you learn it | Next step at techcadd |
|---|---|---|---|
| SOC Monitoring & Triage | Job-ready focus | Foundations | Ready to apply |
| Incident Response | Job-ready focus | Applied Work, capstone | Ready to apply |
| EDR | Strong foundation | Core Skills | Learn on the job |
| Threat Intelligence | Strong foundation | Core Skills | Grow into it from L1/L2 |
| Network Traffic Analysis | Strong foundation | Core Skills | Network Security & CCNA |
| Digital Forensics | Introduced | Capstone write-up | Cyber Forensics |
| Ethical Hacking | Not covered | — | Ethical Hacking or Penetration Testing |
Which SOC Analyst pathsuits you?
SOC work suits people who are patient, notice details and stay calm when something goes wrong. Everyone starts with the same SOC fundamentals; this guide helps if you already have a direction:
| If you… | You will probably enjoy | Typical first job |
|---|---|---|
| Are good at spotting the odd one out in a long list | SOC Monitoring & Triage | SOC Analyst L1 |
| Stay calm under pressure and like following a clear plan | Incident Response | SOC Analyst, then Incident Responder |
| Like reading news about cyber attacks and attacker groups | Threat Intelligence | SOC Analyst, then Threat Intelligence Analyst |
| Enjoy investigating and building a timeline of events | Digital Forensics | Add the Cyber Forensics course |
| Would rather break into systems than watch them | Ethical Hacking | Take Ethical Hacking or Penetration Testing instead |
| Are not sure yet | Start with this course or the Cybersecurity programme | Decide with a counsellor after a free demo class |
Industry-Ready Training in SOC Analyst
- 100% practical, project-based learning
- AI tools integrated into every module
- Live client projects under trainer supervision
- Internship letter and placement support
- Small batches with daily doubt clearing
What you will
actually build
The syllabus is arranged so every module produces an asset rather than a set of notes. You will cover soc fundamentals and the analyst's daily workflow, siem tools and log analysis, incident detection, triage and escalation, threat intelligence and indicator of compromise basics, endpoint detection and response (edr), and finish with a live project built on Splunk, Wireshark, Microsoft Sentinel. Modules run in the order a real project runs: foundations first, then the core skills, then applied work under supervision, then the portfolio and interview preparation that turn all of it into an offer letter.
Foundations
- SOC fundamentals and the analyst's daily workflow
- SIEM tools and log analysis
- Incident detection, triage and escalation
Useful for: SOC Monitoring & Alert Triage, the core of every L1 analyst's day.
SOC Analyst Is Powering the Next Generation of Industry Leaders
- Live client work from week one, supervised by a trainer, not slides, not simulations.
- SOC Analyst (L1/L2) roles in Punjab start around ₹20,000 – ₹32,000 a month for a fresher with a working portfolio.
Reviewed by mentors. Built for interviews.Who can dothis course
The SOC Analyst course is built for people at six different starting points, and the batch is deliberately mixed. What matters far more than your background is turning up consistently and finishing what each module asks you to build.
Students after 12th
Join from any stream. You start from fundamentals with no assumed knowledge, and most students run the course alongside a degree at a Jalandhar college using the weekday or weekend batch.
Graduates and final-year students
If you are finishing a BA, BBA, B.Com, BCA or B.Tech, this is the shortest route from degree to salary. Enter placement season with project work in hand instead of a blank CV.
Working professionals
The weekend batch exists for people already earning. Career switchers typically become interview-ready for SOC Analyst (L1/L2) roles within five to six months without leaving their current job.
Business owners and freelancers
Owners take this course to stop outsourcing work they cannot judge. Freelancers take it to bill clients beyond Punjab, since location does not limit remote work in this field.
Career restarters
A gap on the CV counts for less than work you can point at. The course starts at zero and finishes with a portfolio and a documented internship letter, which is what an interviewer asks about after a break.
Self-taught learners
If free videos left you with notes but nothing built, what changes here is a trainer who reviews what you produced this week and a deadline attached to every module.
One course.A mesh of real tools.
Everything below is installed on the lab machines and used on live client work, not shown once in a slide and forgotten.
- Splunk
- A widely used SIEM for searching and analysing logs
- Wireshark
- Captures network traffic so you can spot unusual patterns
- Microsoft Sentinel
- Microsoft's cloud-based SIEM, common in Azure environments
- CrowdStrike
- An endpoint detection and response (EDR) platform
- MITRE ATT&CK framework
- A public catalogue of attacker techniques analysts map alerts to
Get Certified in
SOC Analyst
Complete the course with a portfolio of live projects and receive an industry-recognised certificate, plus a documented internship letter accepted by Punjab universities.
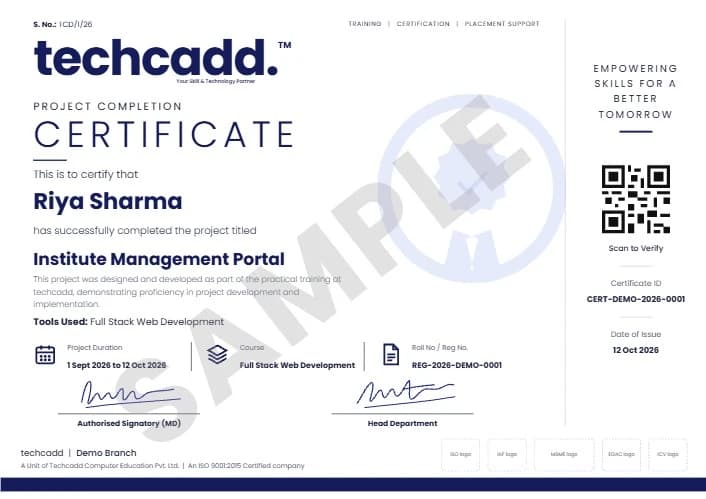
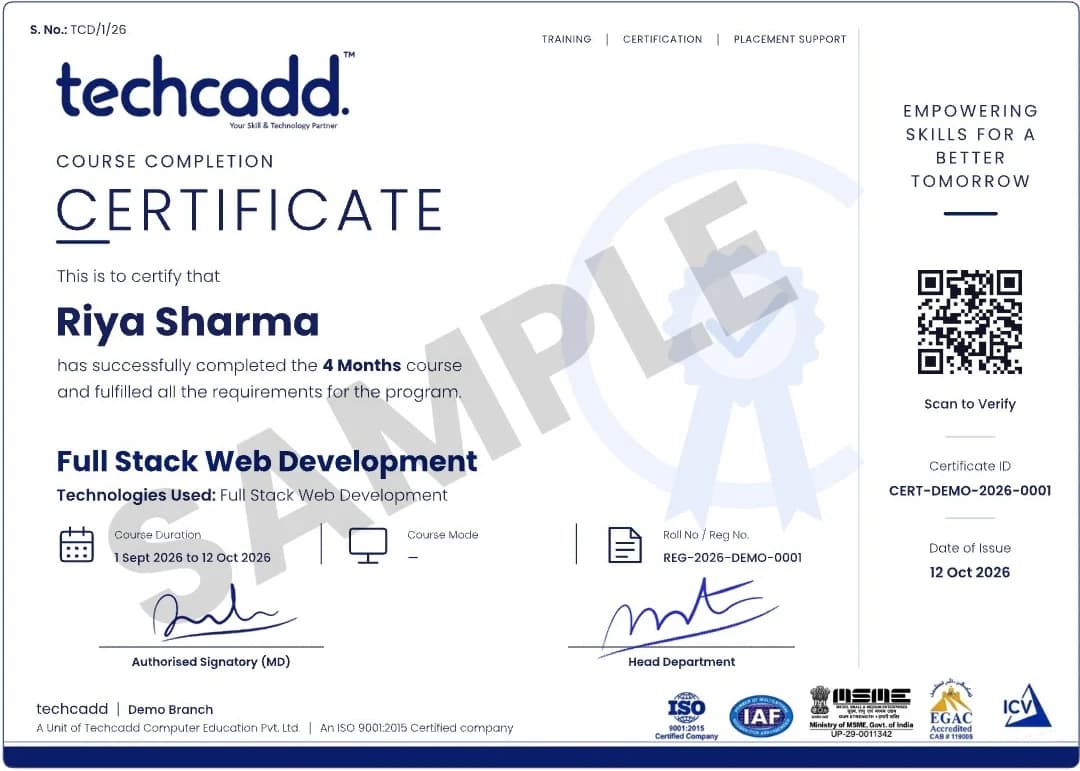
Two certificates on completion — the course certificate and a separate capstone project certificate.
Where this coursetakes you
The roles this opens, what they pay in Punjab and beyond, and who is hiring for them — the same figures our free Salary Estimator publishes, not a brochure number.
What job roles open up after the SOC Analyst course?
SOC teams sit in IT service companies, BPOs, banks and managed security providers, and many hire freshers at L1. The roles fall into two groups:
- SOC Analyst L1
- Security Monitoring Analyst
- Junior Incident Responder
- Security Analyst (junior)
- SOC Analyst L2 / Threat Intelligence Analyst (with experience)
- Digital Forensics Analyst (with Cyber Forensics course)
- Cybersecurity Analyst (with Ethical Hacking course)
- Cloud Security Analyst (with Microsoft Azure or AWS Cloud course)
What job roles open up after SOC Analyst?
Graduates move into SOC Analyst (L1/L2), Security Analyst, Incident Responder, Threat Intelligence Analyst and similar roles. Every mid-sized IT services company and BPO now runs or outsources a SOC, and L1/L2 analyst seats are among the fastest-filled cybersecurity postings in the Tricity and NCR right now.
What can I earn, and how fast does it grow?
A fresher with a working portfolio starts around ₹20,000 – ₹32,000 a month in the Jalandhar market. With two years of delivery experience that typically doubles, and specialists who keep learning move well beyond it.
Can I freelance or work remotely with this skill?
Yes. A Jalandhar address costs you nothing on a remote brief. Students bill clients in Delhi, Dubai and Canada. The course covers client handling, proposals and reporting so you can price and defend your work, not just do it.
Which industries hire for this in Punjab?
Beyond IT companies, the export houses, sports goods and hand tool manufacturers, immigration consultancies, hospitals, schools and real estate firms across Jalandhar all now hire for these skills directly.
Can I continue to higher studies or a specialisation later?
The certificate and portfolio stand on their own, and they stack. Most students move on to an adjacent techcadd track. The tools overlap, so the second course is faster than the first.
Your SOC Analyst careerroadmap
This course is Step 1 for a defensive security career, and for L1 SOC roles it is enough on its own. Specialist roles usually follow experience or one more focused course:
| Goal | Step 1 | Step 2 | Where you arrive |
|---|---|---|---|
| SOC Analyst L1 | SOC Analyst course | Ready to apply | SOC Analyst L1 |
| SOC Analyst L2 / Incident Responder | SOC Analyst course | Experience on a SOC floor | SOC Analyst L2, Incident Responder |
| Threat Intelligence Analyst | SOC Analyst course | Experience on a SOC floor | Threat Intelligence Analyst |
| Digital Forensics Analyst | SOC Analyst course | Cyber Forensics | Digital Forensics Analyst |
| Both attack and defence | SOC Analyst course | Cybersecurity Analyst | |
| Cloud security monitoring | SOC Analyst course | Microsoft Azure or AWS Cloud | Cloud Security Analyst |
Hands-on projectsyou will ship
SOC Analyst Fundamentals Build
Your first working piece, applying soc fundamentals and the analyst's daily workflow and siem tools and log analysis end to end rather than as isolated exercises.
Field: SOC Monitoring & Alert Triage
Real-World Data Challenge
Work with messy, real inputs (threat intelligence and indicator of compromise basics and endpoint detection and response (edr)) and defend the choices you made to a trainer.
Field: Threat Intelligence, EDR
Live Client Brief
A genuine requirement from techcadd's delivery pipeline, scoped, built and shipped under supervision. This is the one interviewers ask about.
Field: SOC operations
Portfolio Capstone
A soc analyst project you specify yourself, covering incident response playbooks and deployment, and present as your final piece.
Field: Incident Response
Learn it. Build it. Make it yours.
Every project moves through the same loop: understand the brief, build with guidance, then explain the decisions behind your work.
Understand
Break a real requirement into a clear plan and the right tools.
SOC Analyst Fundamentals BuildBuild
Work hands-on with trainer feedback while the decisions are still easy to change.
Real-World Data ChallengePresent
Turn the finished work into a portfolio story you can defend in an interview.
Live Client BriefWhy students choosetechcadd
There are many places to learn this in Jalandhar and the brochure syllabus looks similar at all of them. What differs is who teaches, whether you ever touch real work, and whether anyone picks up the phone after you have paid. techcadd has trained students across Punjab since 2016 on the same model: small batches, working practitioners as trainers, client projects as coursework.
Trainers who still do the work
Your trainer is not a full-time lecturer. They deliver client projects for techcadd's services arm, so examples in class are current rather than a case study from five years ago.
Live projects, real consequences
You work on genuine client requirements under supervision. This is where a portfolio comes from, and it is the first thing an interviewer asks to see.
Small batches and open lab hours
Batches stay small enough that a trainer sees your screen daily. Lab time runs outside class hours and doubt sessions continue until the concept lands.
Internship letter and certificate
Every student finishes with an industry-recognised certificate and a documented internship on real work, accepted for university industrial training requirements.
A placement cell that persists
Mock interviews, CV reviews and drives with hiring partners across Jalandhar and Ludhiana, repeated after a rejection, not abandoned.
Since 2016, 25,000+ students
A decade of hiring relationships in Punjab is why a call from our placement cell gets answered and why local employers know what our certificate means.
How techcaddcompares
See how techcadd's SOC Analyst programme stacks up against what you will find at most other institutes in Jalandhar.
| Feature | techcadd | Other institutes |
|---|---|---|
| Training style | 100% practical, hands-on from day one | Mostly theory with occasional demos |
| Projects | Live client work under trainer supervision | Pre-built demo projects or none |
| Batch size | Small batches, trainer sees your screen daily | 30-50 students per batch |
| Trainers | Working professionals who still deliver projects | Full-time lecturers with textbook examples |
| Internship | Documented internship on real client work | Certificate only, no real work exposure |
| Placement support | Dedicated cell, mock interviews, drives until placed | Job portal links or a single drive |
| Doubt clearing | Open lab hours and unlimited doubt sessions | Fixed class hours only |
| Certificate | Industry-recognised certificate + internship letter | Institute certificate only |
What our studentsin Jalandhar say
- Google
The SOC Analyst course got me interview-ready faster than I expected. My interviewer asked to see my project and that was the whole conversation.
Pooja RaniGraduate · Kartarpur GoogleI travelled in for the weekend SOC Analyst batch and it was worth every trip. Small batch, real work, no time wasted on theory nobody uses.
Karan MehtaB.Tech Student · Jalandhar Googletechcadd's placement cell kept calling me for drives until I was placed. That persistence mattered more than the certificate for SOC Analyst.
Sandeep KaurPlaced Fresher · Phillaur GoogleThe SOC Analyst course got me interview-ready faster than I expected. My interviewer asked to see my project and that was the whole conversation.
Pooja RaniGraduate · Kartarpur GoogleI travelled in for the weekend SOC Analyst batch and it was worth every trip. Small batch, real work, no time wasted on theory nobody uses.
Karan MehtaB.Tech Student · Jalandhar Googletechcadd's placement cell kept calling me for drives until I was placed. That persistence mattered more than the certificate for SOC Analyst.
Sandeep KaurPlaced Fresher · Phillaur
- Google
I was switching careers and worried I would be behind. Half the SOC Analyst batch were doing the same thing, and nobody made me feel slow.
Harpreet KaurSoftware Trainee · Jalandhar GoogleI joined the SOC Analyst batch with almost no background and finished with a project I could actually show. The trainers correct your work daily rather than just moving to the next slide.
Rohit SharmaJunior Analyst · Phagwara GoogleWhat made SOC Analyst click for me was the lab time. You can sit after class and someone will still explain it until you get it.
Simranjeet SinghFreelancer · Kapurthala GoogleI was switching careers and worried I would be behind. Half the SOC Analyst batch were doing the same thing, and nobody made me feel slow.
Harpreet KaurSoftware Trainee · Jalandhar GoogleI joined the SOC Analyst batch with almost no background and finished with a project I could actually show. The trainers correct your work daily rather than just moving to the next slide.
Rohit SharmaJunior Analyst · Phagwara GoogleWhat made SOC Analyst click for me was the lab time. You can sit after class and someone will still explain it until you get it.
Simranjeet SinghFreelancer · Kapurthala
Choose howyou want to learn
Every mode covers the same syllabus, projects and placement support. Pick the schedule that fits your life.
Classroom Training
Learn in techcadd's air-conditioned labs with licensed software, a projector and a trainer who sees your screen daily. Weekday batches run Monday to Friday, 2 hours per session.
Learn moreOnline Live Classes
Join live instructor-led sessions from anywhere. Screen sharing, real-time doubt clearing and the same assignments as the classroom batch, with recordings available for 7 days.
Learn moreWeekend Batches
Saturday and Sunday batches for working professionals and college students. Same syllabus, same projects, same placement support — just a different calendar.
Learn more1-on-1 Personal Training
Set your own schedule with a dedicated trainer. Ideal for professionals with shifting rosters or anyone who wants to move faster than a batch allows.
Learn moreFrequently Asked Questions
techcadd runs SOC Analyst over 3 to 6 months depending on the track you choose. Weekday, evening and weekend batches cover the same syllabus, and 1-on-1 training is available if you would rather set your own pace. Every class runs for 2 hours, whichever format you choose.
Fees depend on the course length and subject. techcadd counsellors share the exact fee for the length you choose and EMI options on request, and a demo class is free.
Students after 12th, graduates and final-year students, working professionals switching careers, and business owners all join this course. You start from fundamentals, so a technical background helps but is not required.
Graduates typically move into roles such as SOC Analyst (L1/L2), Security Analyst, Incident Responder or Threat Intelligence Analyst. Every mid-sized IT services company and BPO now runs or outsources a SOC, and L1/L2 analyst seats are among the fastest-filled cybersecurity postings in the Tricity and NCR right now.
A fresher with a working portfolio typically starts around ₹20,000 – ₹32,000 per month in the Jalandhar market, rising substantially within two years of experience. Freelancers handling multiple clients often earn more, since remote work is not limited by location.
No training provider can honestly guarantee a job, and you should be cautious of anyone in Jalandhar who claims one. techcadd guarantees placement support: CV reviews, mock interviews, portfolio preparation and repeated drives with hiring partners across Jalandhar and Ludhiana.
You will work hands-on with Splunk, Wireshark, Microsoft Sentinel, CrowdStrike, MITRE ATT&CK framework and the supporting toolchain used on live projects. All practice happens in the lab on licensed software, not on demo screenshots.
Yes. Every student receives an industry-recognised certificate on completion plus a documented internship letter based on live client work. The internship satisfies the industrial training requirement at most Punjab universities.
Every module ends with something you built. Best SOC Analyst Course & Training in Jalandhar finishes with a live project drawn from techcadd's own client delivery work, supervised by a trainer, which becomes the portfolio you take to interviews.
Yes. techcadd Jalandhar runs weekday, evening and weekend batches in parallel so working professionals and college students can both attend, and 1-on-1 training is available for a fully personal schedule. Every class (batch or 1-on-1) runs for 2 hours; book a free demo class to see the lab and meet the trainer before enrolling.
No. A SOC analyst defends: monitoring alerts, investigating and responding. An ethical hacker attacks with permission to find weaknesses. This course is entirely defensive; offensive skills are taught in techcadd's Ethical Hacking and Penetration Testing courses.
Often, yes. Many SOCs run 24×7, so analysts work in rotating shifts, especially at L1. Some in-house SOCs at banks or companies work business hours. It is worth asking about shifts at every interview.
Yes. SIEM tools and log analysis are part of the first module, using Splunk and Microsoft Sentinel, along with the MITRE ATT&CK framework that analysts use to describe what an attacker is doing.
They are related but different. A SOC analyst detects and responds to incidents quickly. A forensics analyst investigates in depth afterwards and handles evidence so it holds up in legal or corporate proceedings. Forensics is taught in techcadd's Cyber Forensics course.
No. L1 work is mostly reading alerts and logs and following playbooks. Searching and reading logs in a SIEM is part of the course. Scripting in Python helps later for automation, and can be added with techcadd's Python course.
Not sure which security path is right for you?
Tell a counsellor whether you would rather watch for attacks, investigate them or test systems yourself, and we will show you whether this SOC course, Ethical Hacking or the full Cybersecurity programme suits you. Book a free demo class and see the lab first.
Ask aboutSOC Analyst
Send your question and a counsellor will call you back about batch timings, fees, EMI options, placement record, or whether this course fits your degree.
- Free counselling and demo class
- Weekday, evening, weekend or 1-on-1, all 2-hour classes
- Internship letter and placement support